
 Clarissa Hana
A sophisticated phishing-as-a-service (PhaaS) framework, dubbed BigBear 2.0, has achieved a significant breach, successfully circumventing multi-factor authentication (MFA) at 258 organizations and compromising over 5,000 Microsoft 365 credentials. This alarming development, uncovered by cybersecurity researchers at CloudSEK, highlights a critical vulnerability in common security protocols and the evolving tactics of cyber adversaries. The BigBear 2.0 service, operating through a network of compromised infrastructure, has demonstrated a disturbing proficiency in hijacking authenticated user sessions, thereby gaining access to sensitive corporate data and resources.
The Anatomy of the BigBear 2.0 Attack
Researchers at CloudSEK gained unauthorized access to the control panel of the BigBear 2.0 service, revealing its extensive operational capabilities. The analysis showed the framework managed 42 distinct Virtual Private Server (VPS) nodes, all meticulously configured to target Microsoft 365, a widely adopted suite of cloud-based productivity and identity services. These services include Exchange Online for email, Teams for communication, SharePoint and OneDrive for collaboration and file storage, and Entra ID (formerly Azure Active Directory) for authentication.
At the core of BigBear 2.0’s modus operandi is its utilization of an adversary-in-the-middle (AiTM) framework, specifically an adaptation of Evilginx2. This technique allows attackers to position themselves between the victim and the legitimate Microsoft 365 authentication servers. When a user attempts to log in, the phishing service intercepts their credentials, including the one-time codes or biometric prompts associated with MFA. Crucially, BigBear 2.0 doesn’t merely steal credentials; it captures authenticated session cookies. These cookies act as digital passports, allowing attackers to hijack the user’s active session without needing to re-authenticate, even after MFA has been ostensibly satisfied.
The service employs a specific configuration, referred to as "offy," to establish this man-in-the-middle proxy. This proxy effectively tricks the victim into interacting with a fraudulent authentication page that mirrors the legitimate Microsoft 365 login portal. Once the victim enters their username and password, and subsequently completes the MFA challenge, the attacker’s proxy captures both the credentials and the valid session cookie. This cookie is then replayed through an API, enabling the attacker to bypass security checks and gain access to the victim’s account as if they were the legitimate user.
Scale and Scope of the Compromise
The exfiltration data gathered by CloudSEK paints a stark picture of the campaign’s reach and impact. The control panel revealed a staggering haul of 5,137 credential records. This includes 474 instances where MFA was successfully bypassed, 1,032 plaintext passwords, and 4,148 session cookies. These compromised accounts belong to users across 3,331 unique IP addresses, spanning over 40 countries. At the time of CloudSEK’s reporting, the operation was still actively engaged in further attacks.
While a broader targeting dataset identified 461 organizations potentially subjected to BigBear 2.0’s efforts, CloudSEK’s detailed analysis confirmed that 258 distinct organizations suffered at least one completed MFA-bypass compromise. This indicates a highly effective and targeted campaign against entities utilizing Microsoft 365.
Advanced Evasion Techniques
BigBear 2.0 employs several advanced techniques to enhance its success rate and evade detection. To bypass the increasingly robust FIDO2/WebAuthn authentication methods, the platform injects custom JavaScript into the phishing pages. This malicious script interferes with the browser’s functionality, effectively disabling the browser-based prompts for FIDO2/WebAuthn, thereby coercing victims into resorting to weaker authentication methods like passwords and SMS-based MFA, which are more susceptible to phishing.
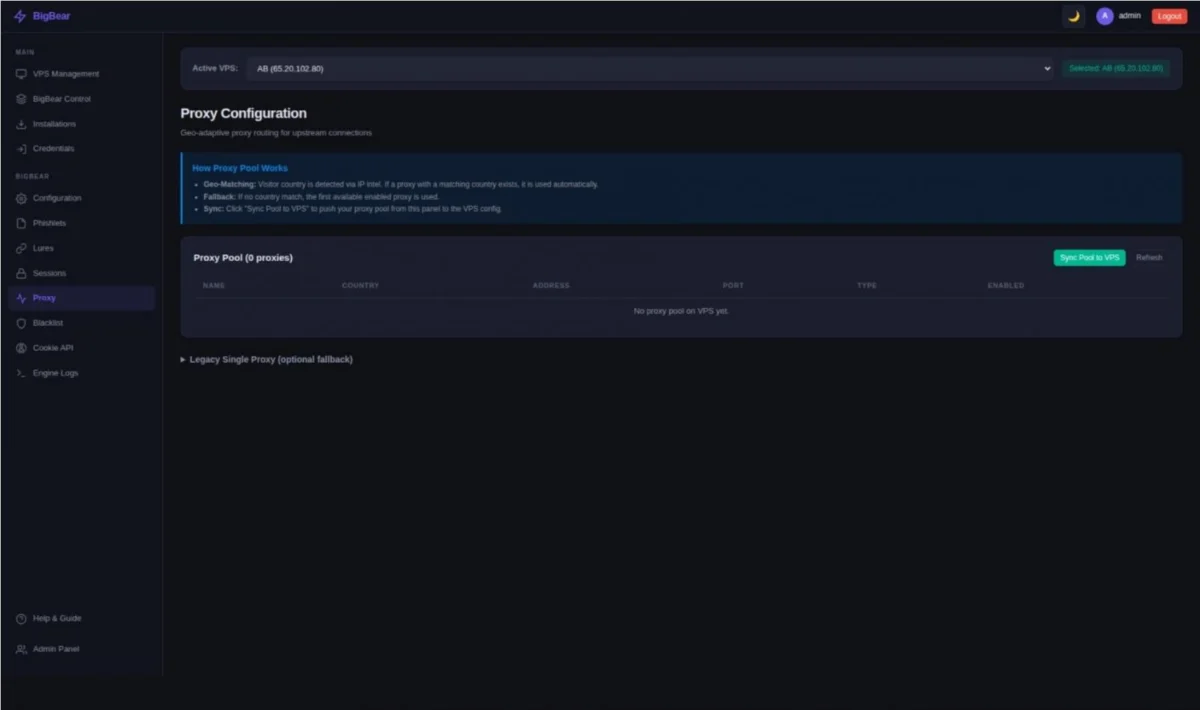
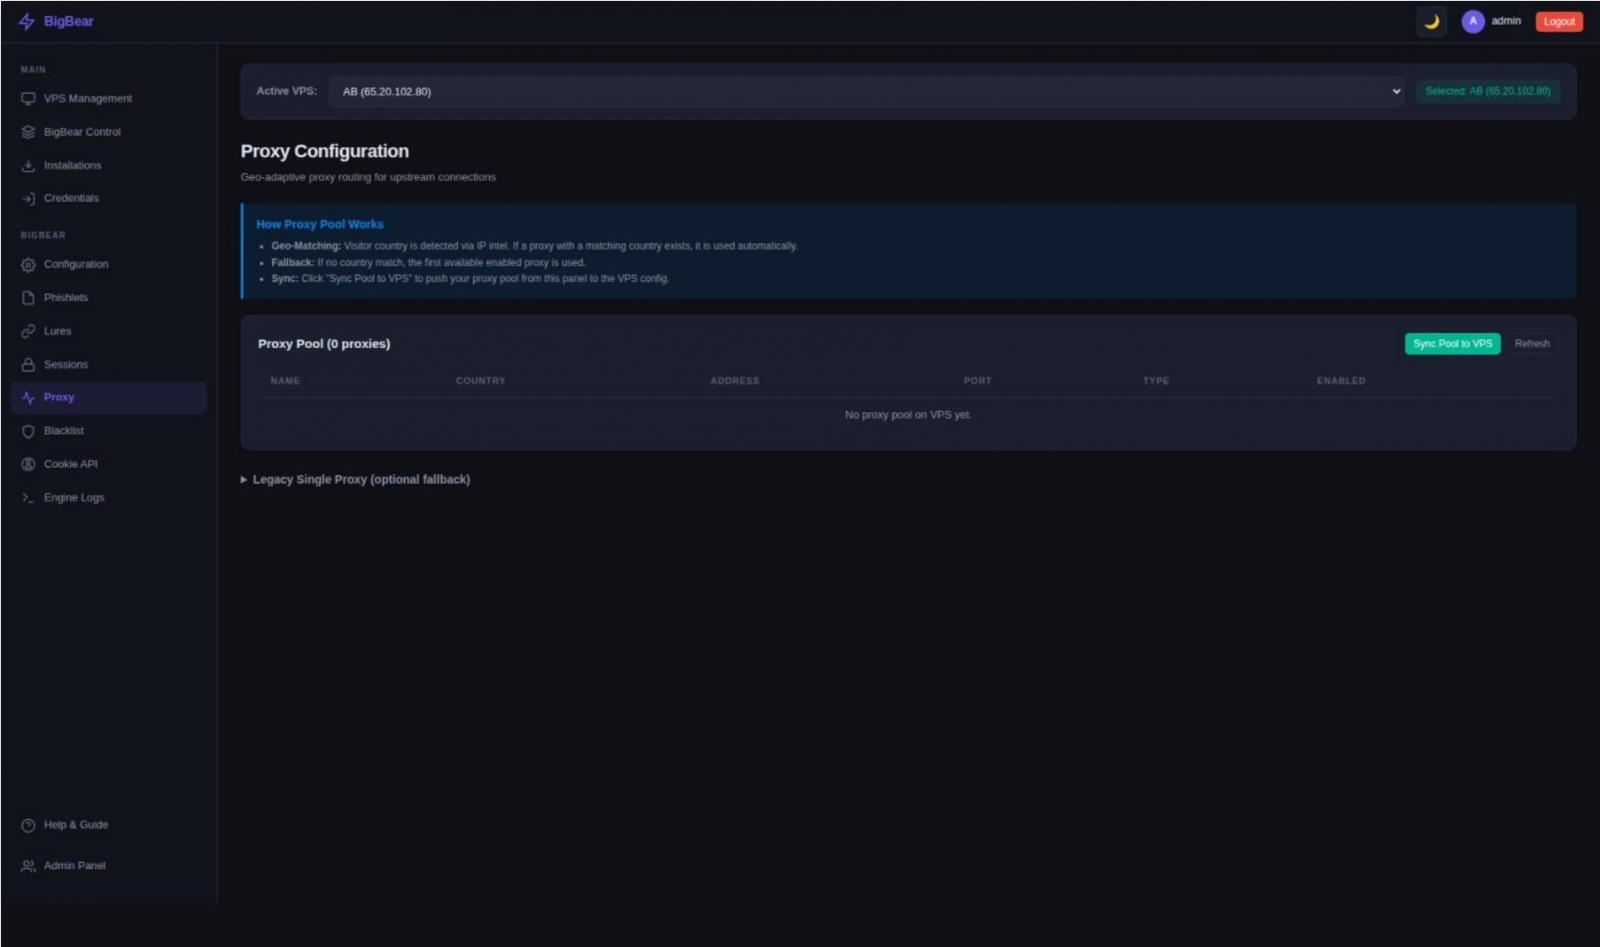
Furthermore, the service leverages geo-matched residential proxies to mask its malicious traffic. By utilizing IP addresses that correspond to the victim’s geographical location and are associated with legitimate residential internet connections, BigBear 2.0 makes it significantly harder for Microsoft’s authentication servers to flag the suspicious activity. This sophisticated proxying strategy helps the phishing infrastructure blend seamlessly with normal network traffic, reducing the likelihood of immediate detection. The control panel itself provides options for configuring these proxies, further illustrating the service’s user-friendly approach for its operators.
The Phishing-as-a-Service Model
The "Phishing-as-a-Service" (PhaaS) model underpinning BigBear 2.0 is a critical factor in its widespread impact. The multi-user panel is leased to multiple affiliate operators, identified by CloudSEK through live Telegram exfiltration bots. These bots receive stolen credentials in real-time, indicating a well-oiled criminal enterprise where stolen data is immediately monetized or exploited. This model democratizes sophisticated cybercrime, allowing individuals with limited technical expertise to launch large-scale, effective phishing campaigns.
Background and Chronology of the Campaign
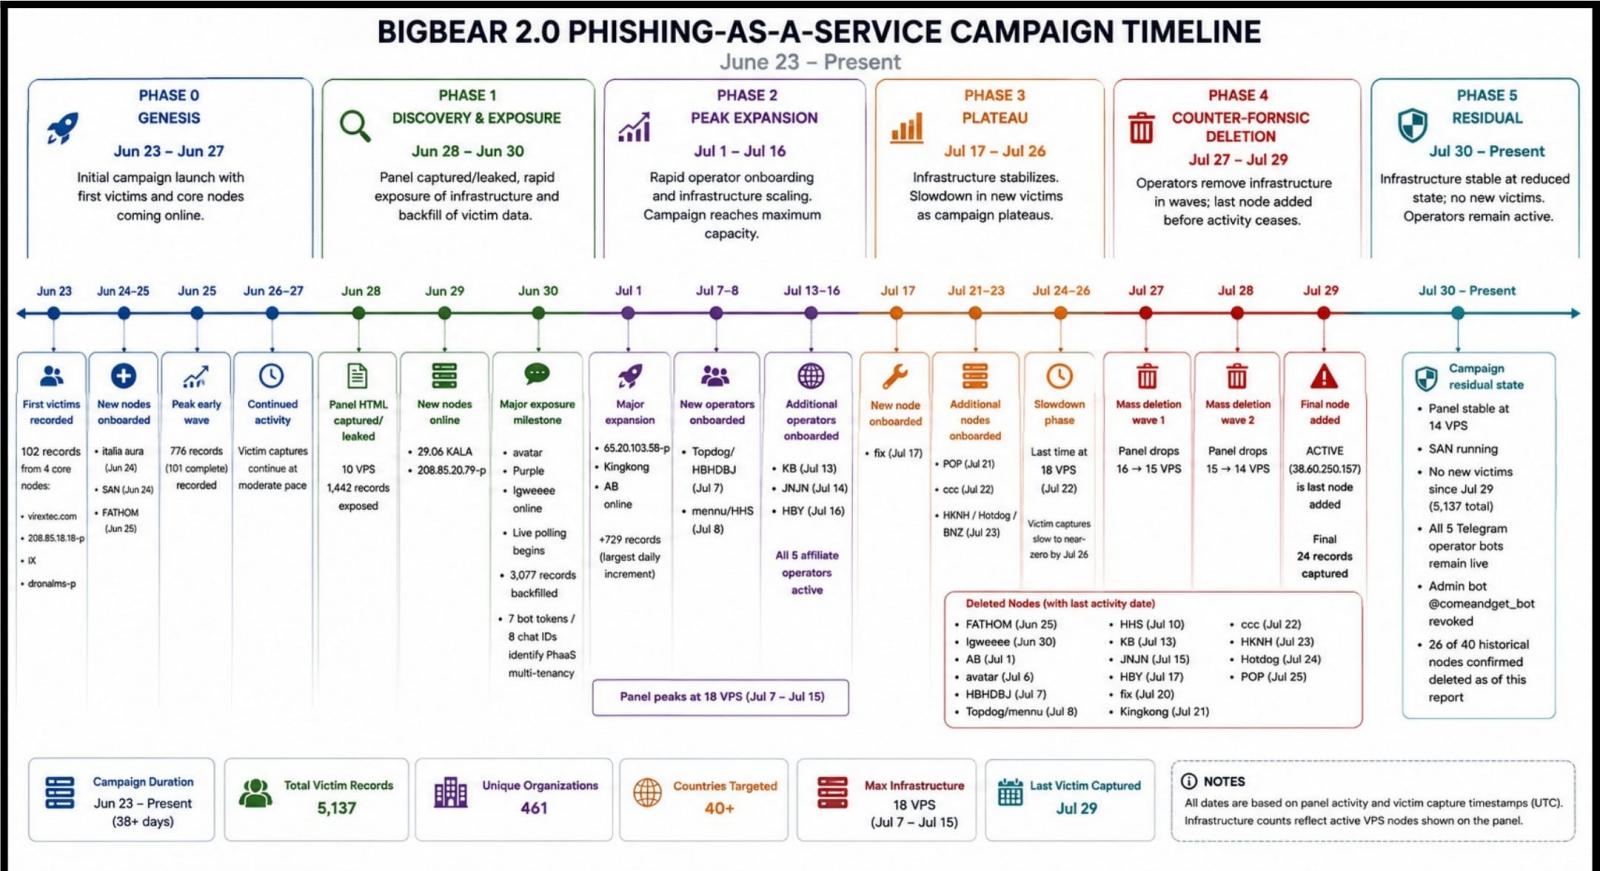
The emergence of BigBear 2.0 builds upon a history of sophisticated phishing operations. Evilginx2, the underlying AiTM framework, has been in circulation for several years, continuously evolving to counter security measures. CloudSEK’s analysis of the BigBear 2.0 campaign, as depicted in their provided timeline, suggests a sustained period of activity. While the exact commencement date of this specific BigBear 2.0 iteration remains under investigation, the operational infrastructure’s recent offline status, lasting nearly three weeks at the time of reporting, implies a significant, albeit potentially temporary, disruption. The fact that the administration panel remained online while the phishing infrastructure was down suggests that the service operators may be migrating or rebuilding their attack infrastructure.
The broader context of this attack lies within the escalating threat landscape targeting cloud services. As organizations increasingly rely on platforms like Microsoft 365 for critical operations, these services become prime targets for cybercriminals seeking to gain access to valuable data and maintain persistent footholds within corporate networks. The bypass of MFA, long considered a cornerstone of modern security, signals a dangerous advancement in attacker capabilities.
Implications for Organizations and Users
The success of BigBear 2.0 in bypassing MFA has profound implications for cybersecurity strategies. It underscores that no security measure is infallible and that a layered approach is essential. Compromising an authenticated Microsoft 365 session can lead to severe consequences, including the exposure of sensitive emails, confidential files stored on OneDrive and SharePoint, and potentially access to other integrated applications through single sign-on. For organizations, this can translate to data breaches, financial losses, reputational damage, and regulatory penalties.
For individual users, the compromise of their accounts can lead to identity theft, financial fraud, and the misuse of their professional or personal communications. The ease with which session cookies can be hijacked means that even after a successful MFA prompt, an attacker can maintain access for an extended period, making detection and remediation more challenging.
Official Responses and Recommendations
CloudSEK has taken proactive steps by notifying law enforcement agencies and several of the affected organizations. They have also included the compromised credentials in responsible-disclosure reports, a standard practice in the cybersecurity community to allow for remediation before widespread public disclosure.
In response to such sophisticated attacks, cybersecurity experts recommend several critical actions for organizations:
- Password Resets and Session Revocation: Immediately reset all passwords for accounts that may have been exposed. Additionally, revoke all active sessions and refresh authentication tokens to force users to re-authenticate.
- Enforce Phishing-Resistant MFA: Prioritize the adoption of phishing-resistant MFA methods, such as FIDO2/WebAuthn security keys, over less secure options like SMS-based codes.
- Implement Conditional Access Policies: Leverage Microsoft Entra ID’s Conditional Access policies to enforce stricter access controls. Requiring managed devices for access and implementing real-time risk detection can significantly bolster security.
- User Education and Awareness: Continuous training and awareness programs for employees are crucial to help them recognize and report phishing attempts.
- Security Monitoring and Threat Intelligence: Maintain robust security monitoring capabilities to detect anomalous login activity and unusual data access patterns. Subscribing to threat intelligence feeds can provide early warnings of emerging threats.
The Ongoing Battle
Despite the recent disruption to its phishing infrastructure, the BigBear 2.0 administration panel reportedly remained online at the time of CloudSEK’s report, indicating the resilience and adaptability of these cybercriminal operations. The continuous evolution of phishing techniques, particularly those targeting MFA, necessitates a constant vigilance and an adaptive security posture. The BigBear 2.0 campaign serves as a potent reminder that the digital battleground is constantly shifting, and staying ahead of threats requires ongoing innovation in both offensive and defensive cybersecurity strategies. The data from the "Blue Report 2026" further emphasizes this, indicating that once attackers gain valid credentials, the effectiveness of security defenses drops significantly, highlighting the critical importance of preventing initial access and robust post-compromise containment.








