Clarissa Hana
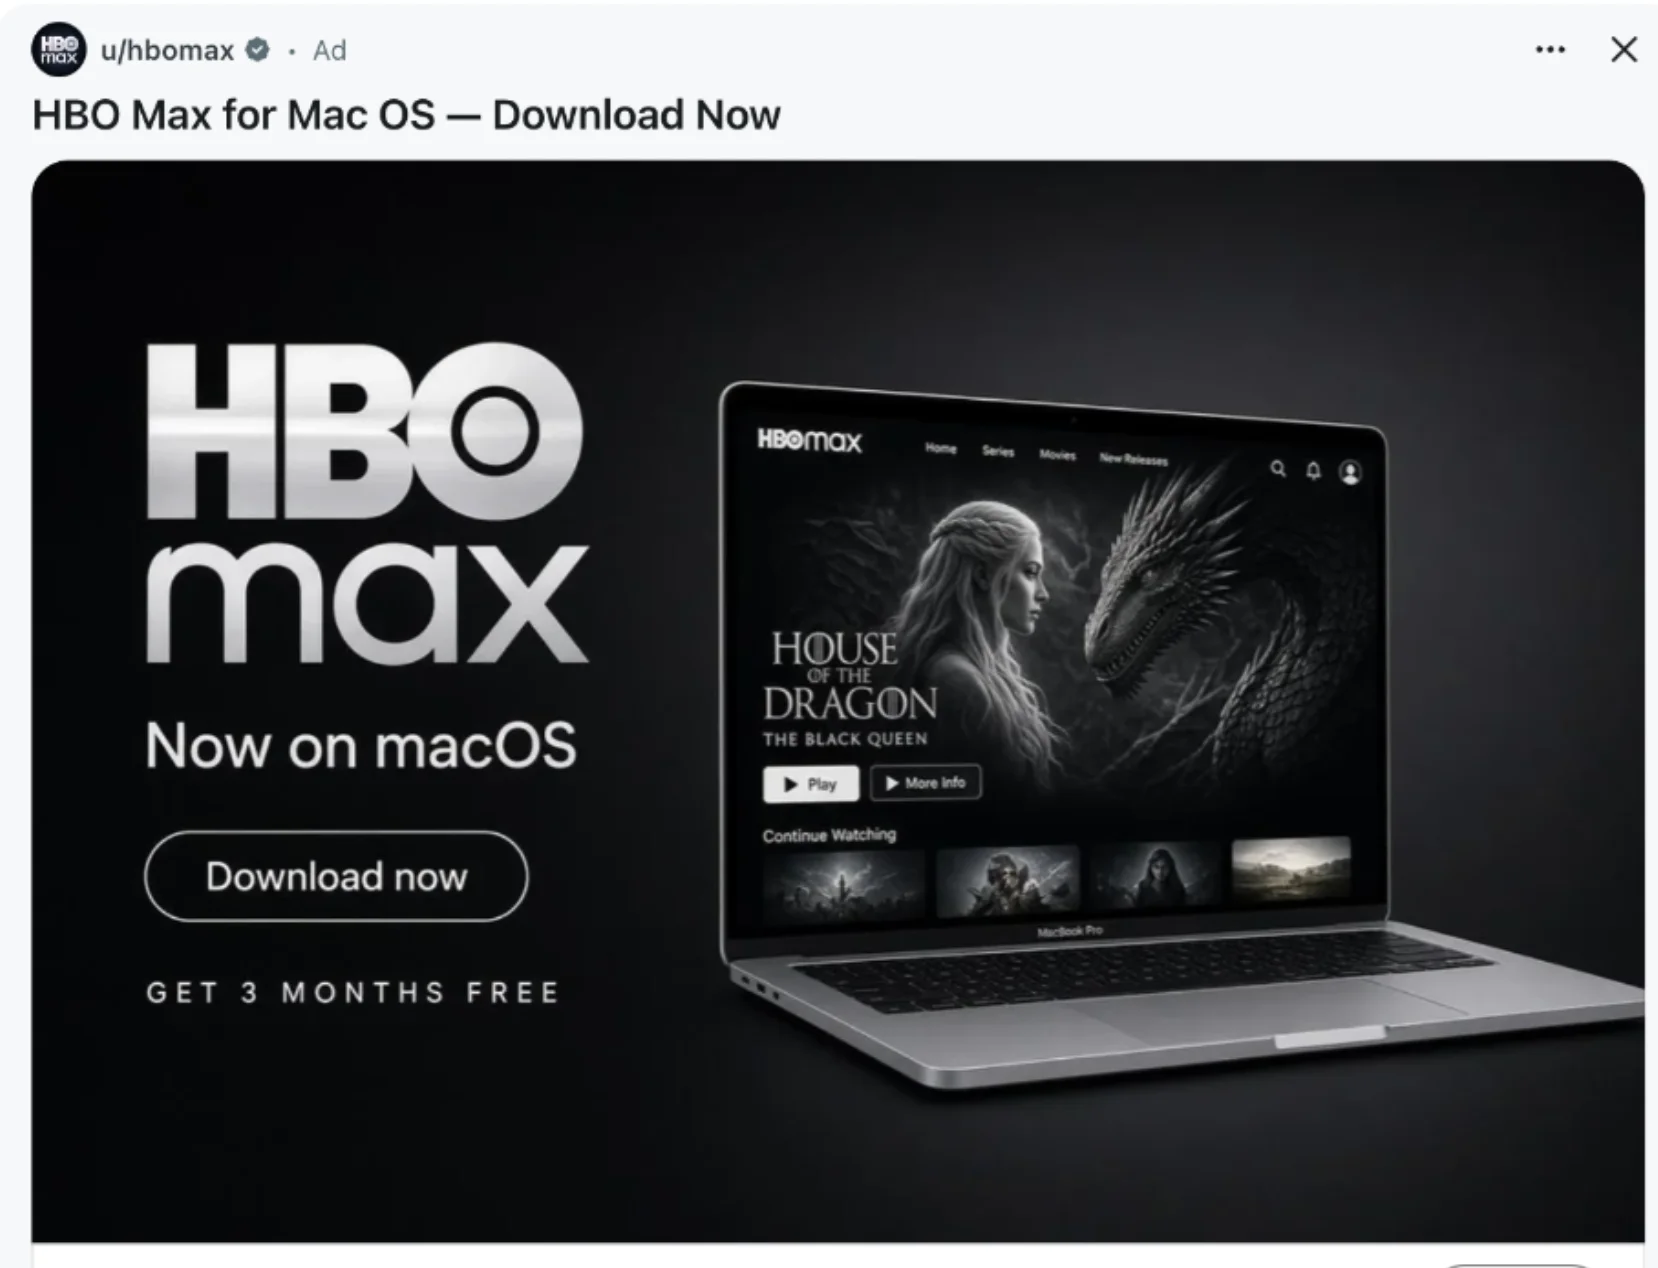
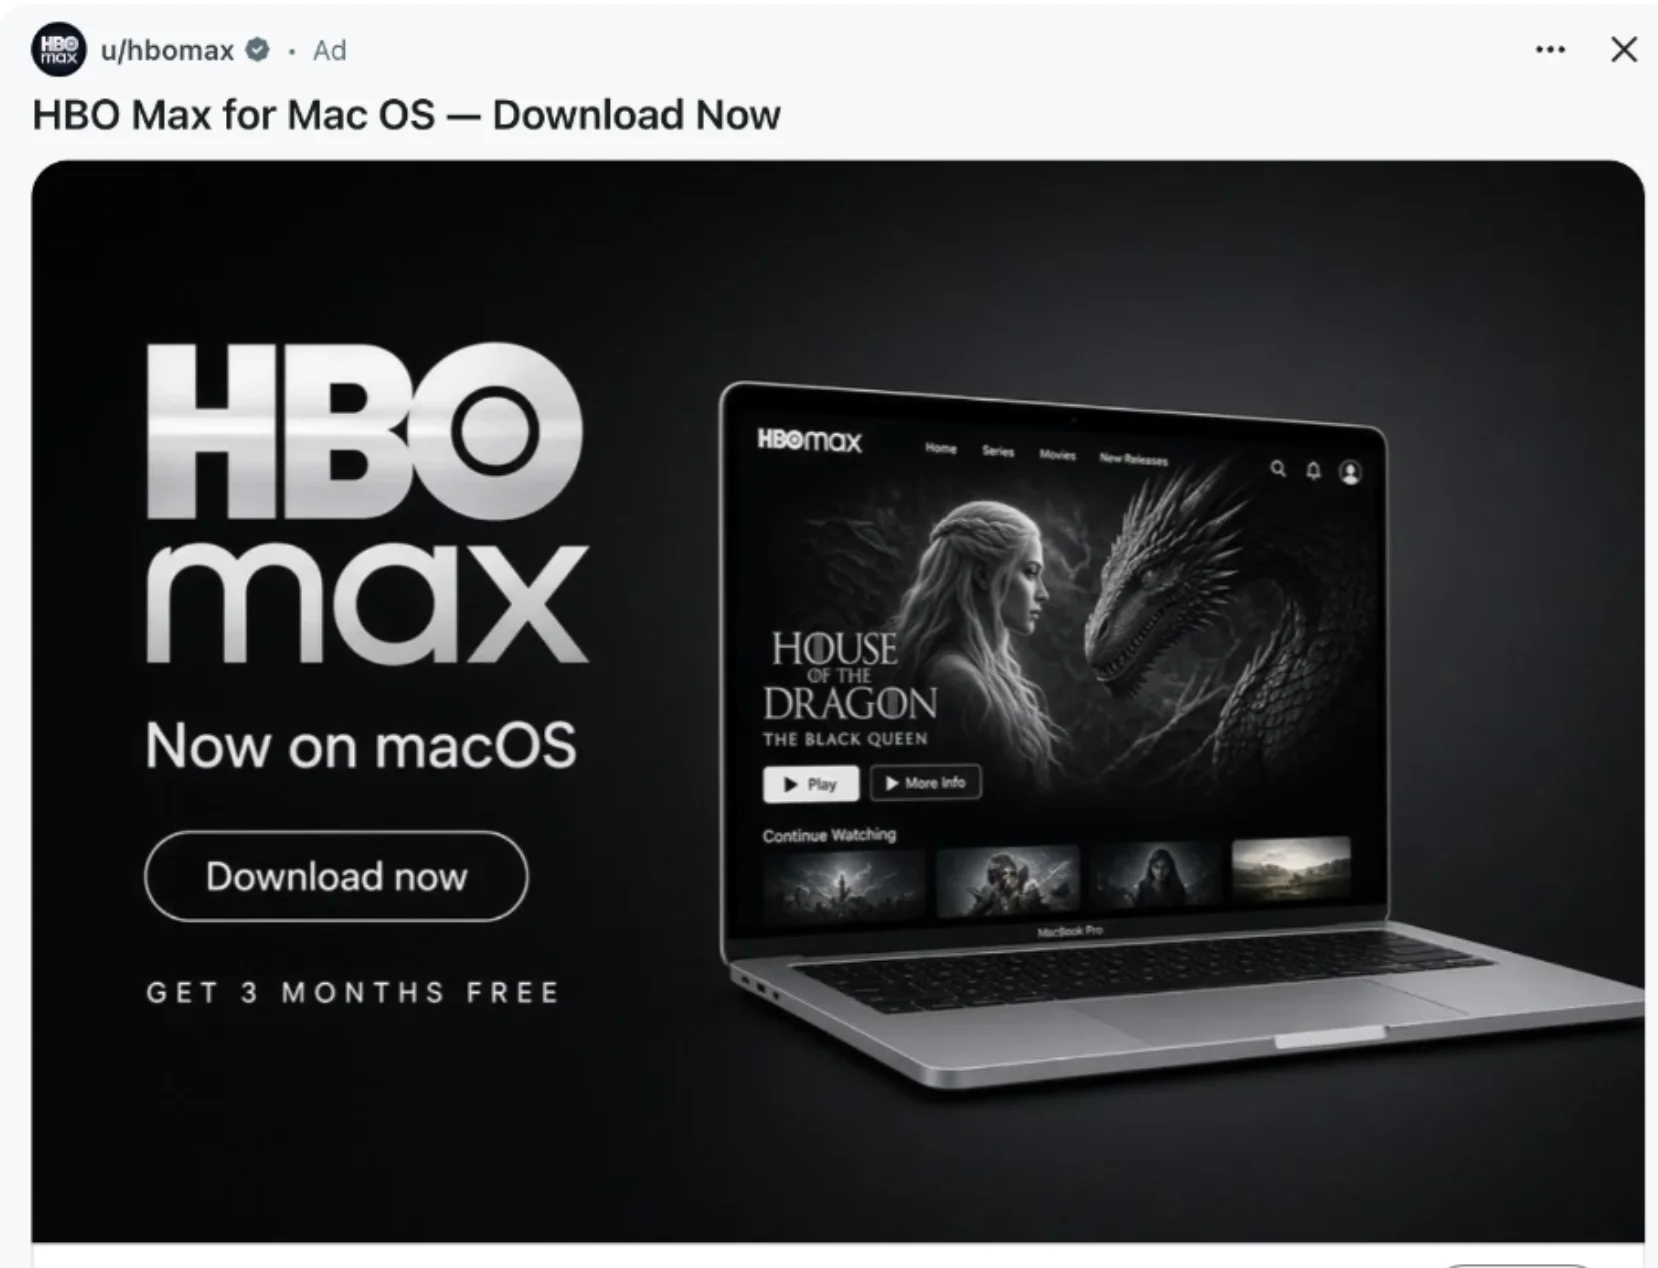
In a sophisticated cyberattack that underscores the evolving tactics of threat actors, hackers successfully compromised the official HBO Max Reddit account, weaponizing it to disseminate malicious advertisements. These ads, disguised as legitimate content, employed a social engineering technique known as "ClickFix" to trick unsuspecting users into executing commands that installed information-stealing malware on both Windows and macOS devices. The operation, analyzed by security researchers from Hudson Rock and ADAMnetworks, exposed a significant campaign dubbed "PasteSwitch," which leverages compromised platforms and deceptive practices to target a wide range of users. The attack, which ran for approximately 48 hours, saw the verified u/hbomax Reddit account used to launch 108 malicious advertisements, highlighting a brazen exploitation of a trusted brand’s online presence.
The Mechanics of the ClickFix Attack
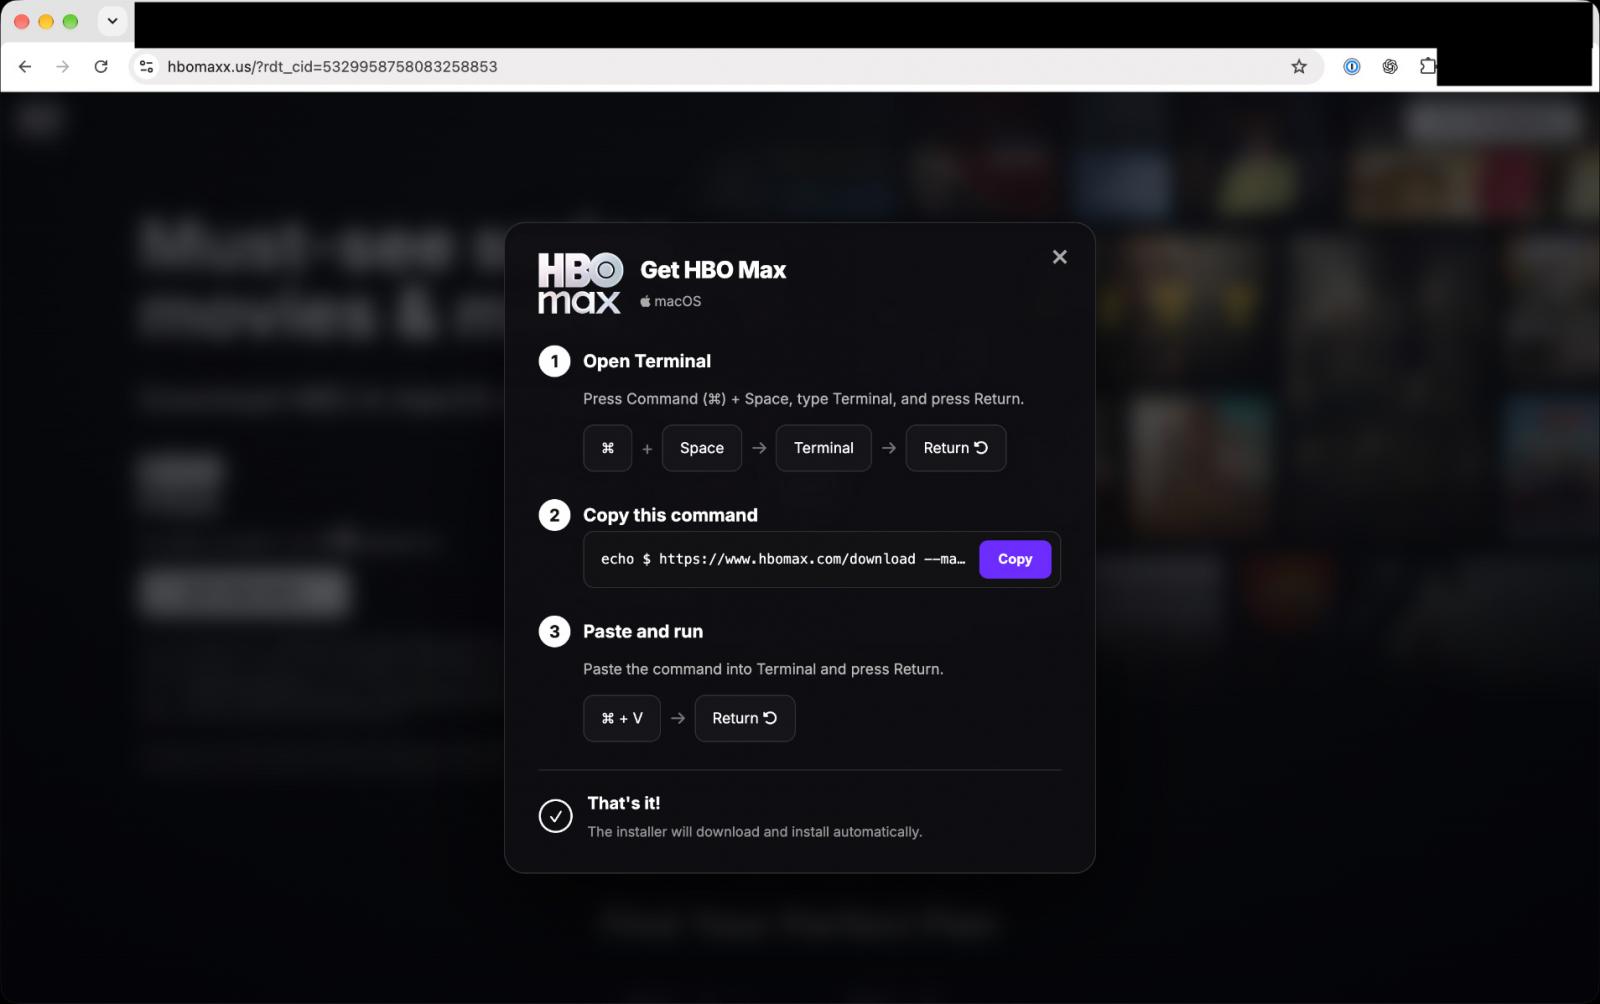
The core of this cyber offensive relied on the ClickFix social engineering method. This technique preys on users’ desire to resolve perceived issues or access desired content. Attackers craft messages that prompt users to copy and paste commands into their system’s command-line interfaces, such as Windows Run, PowerShell, or macOS Terminal. These commands are often presented as solutions to errors, steps to verify a CAPTCHA, or instructions to install seemingly legitimate software. The insidious nature of ClickFix lies in its ability to circumvent traditional security measures. By having the victim manually execute commands using built-in operating system tools, the malware often bypasses browser-based malware detection systems and security software designed to flag suspicious downloads. This method effectively turns the user into an unwitting accomplice in their own system’s compromise.
The PasteSwitch Operation: A Broader Threat Landscape
The advertisements pushed through the compromised HBO Max Reddit account were not solely focused on impersonating the streaming service. While some ads promoted a fake HBO Max application for macOS, others advertised a variety of deceptive offerings, including fake Artificial Intelligence (AI) tools, developer software, and macOS system utilities. This diversification of lures suggests a strategic effort to cast a wider net, appealing to a broader spectrum of internet users beyond just fans of the streaming platform.
Security researchers have linked this incident to a larger, ongoing cyber operation known as PasteSwitch. This extensive campaign targets both Windows and macOS systems and is characterized by its versatile payload delivery. PasteSwitch has been observed distributing a range of malicious software, including information stealers, loaders designed to download further malware, cryptocurrency clippers that intercept and redirect cryptocurrency transactions, and counterfeit cryptocurrency wallet applications. The name "PasteSwitch" aptly describes the operation’s methodology: victims are enticed to "paste" attacker-supplied commands into their systems, while the attackers’ backend infrastructure dynamically "switches" between different campaigns, target platforms, malware payloads, and cryptocurrency theft methods based on the profile of the visiting user. This adaptive approach makes PasteSwitch a particularly challenging adversary to track and defend against.
Chronology of the Attack and Discovery
The malicious campaign began to surface around the time a Reddit user noticed an advertisement appearing from the verified HBO Max account. This ad purported to promote a native HBO Max application for macOS, a product that was not widely known or officially announced, sparking the user’s curiosity. The user, who later shared their findings on Reddit and cybersecurity forums, noted the legitimacy of the account verification and the account’s posting history within official HBO Max subreddits, which lent a false sense of trust to the advertisement.
The user’s investigation revealed that clicking the advertisement directed them to a convincing, albeit fake, website registered as hbomaxx[.]us. This domain was designed to mimic the official HBO Max branding, complete with a "Join" or "Download" button. Upon interaction with these buttons, instead of downloading an application, users were presented with instructions to open their system’s Terminal and paste a specific command. This command, often obfuscated using techniques like Base64 encoding, was the gateway to malware installation. One observed macOS command, once decoded, revealed a process involving curl to download a shell script from ember-bridge[.]com, which was identified by Hudson Rock as prior infrastructure used in PasteSwitch operations for malware delivery.
Malware Families and Capabilities
The PasteSwitch operation, as evidenced by the HBO Max Reddit incident, deploys a variety of sophisticated malware. On macOS, one identified family is MacSync, which specializes in exfiltrating sensitive user data. This includes browser credentials, Firefox profiles, Telegram chat data, Apple Notes, and macOS system passwords. Another macOS threat observed is "AMOS helper," a piece of malware designed to establish persistence on infected systems. It achieves this by creating a directory named .com.apple.accountsd and then enrolls the compromised machine with attacker-controlled servers. This allows the attackers to remotely issue further commands and tasks to the infected device, effectively turning it into a bot.
The campaign has also been instrumental in distributing counterfeit cryptocurrency wallet applications. Fake versions of popular wallets like Ledger, Trezor Suite, and Exodus are presented to users, with the malicious intent of stealing their critical wallet recovery phrases, granting attackers direct access to their digital assets.
For Windows systems, PasteSwitch employs different, yet equally dangerous, attack vectors. Instructions often guide victims to execute commands via mshta and PowerShell. One observed Windows attack chain utilized an MP3/HTA polyglot file. This cleverly crafted file functions as both an audio file and a Windows HTA (HTML Application) file, allowing it to execute malicious code. The executed code then proceeds to create a scheduled task, launch a 32-bit PowerShell instance, disable Microsoft’s Antimalware Scan Interface (AMSI) – a key security feature designed to detect and block malicious scripts – and generate victim-specific infrastructure based on unique system identifiers like the computer name and username. Subsequent stages of the attack often involve heavily obfuscated PowerShell scripts and shellcode designed to load information-stealing malware, such as Amatera Stealer, directly into the system’s memory without writing the final payload to disk, making detection even more challenging.
Furthermore, PasteSwitch has been observed distributing cryptocurrency clipboard hijacking malware, including variants like AnimateClipper and ZigClipper. These types of malware monitor the user’s clipboard. When a cryptocurrency address is copied, the malware discreetly replaces it with an attacker-controlled address, ensuring that any transaction made will be sent to the hacker instead of the intended recipient.
The Breadth of the Advertising Campaign
The malicious advertisements originating from the compromised HBO Max Reddit account were part of a much larger, coordinated effort. Researchers identified a significant volume of ads pointing to various malicious domains: 40 ads directed users to hbomaxx[.]app, 36 promoted a fake AI and developer site at codex-craft[.]com, 15 advertised apple.clean-disk-guide[.]com, 11 led to code-desktop[.]com, and six promoted hbomax-macos[.]com. This extensive network of fake websites and domains allowed the attackers to target a diverse audience, not just HBO Max subscribers but also individuals actively searching for AI software, developer tools, and system utilities. This broad targeting strategy maximizes the potential reach and impact of the PasteSwitch operation.
Official Responses and Broader Implications
BleepingComputer reached out to HBO and Warner Bros. Discovery for comment regarding the compromise of their official Reddit account and the subsequent misuse for malicious advertising. As of the time of reporting, no response had been received. The lack of immediate public statement leaves many questions unanswered, including the method of account compromise and whether any other HBO or Warner Bros. Discovery digital assets were affected.
The incident serves as a stark reminder of the persistent threats posed by sophisticated cybercriminal operations. The exploitation of a trusted brand’s social media presence to distribute malware highlights the increasing sophistication and audacity of attackers. Verified accounts on platforms like Reddit, typically seen as reliable sources of information, can be turned into vectors for widespread compromise.
The ClickFix technique, combined with the adaptable nature of the PasteSwitch operation, presents a significant challenge for cybersecurity professionals. It emphasizes the need for users to exercise extreme caution when encountering unexpected advertisements or prompts, even those appearing to originate from reputable sources. Vigilance, skepticism, and a thorough understanding of common social engineering tactics are crucial defense mechanisms in navigating the increasingly complex digital landscape.
The successful operation also points to potential vulnerabilities in the account security protocols of major platforms and the oversight mechanisms for advertising content. While Reddit admins did eventually pause the malicious advertisements and report the issue to their security teams, the initial period of unchecked distribution allowed for significant potential damage. This incident underscores the ongoing need for robust security measures, rapid incident response capabilities, and continuous monitoring to protect users from evolving cyber threats. The broader implications extend to all organizations that utilize social media for brand engagement, as the potential for account compromise and subsequent misuse remains a critical concern. The ability of attackers to leverage seemingly legitimate channels to deploy advanced malware demands a proactive and layered approach to cybersecurity for both individuals and corporations alike.