Sonny Valindra
Comp AI, a burgeoning startup at the forefront of cybersecurity and compliance solutions, announced on Thursday the successful closure of its $34 million Series A funding round. This significant investment, spearheaded by prominent venture capital firms Roo Capital and Grand Ventures, underscores the growing demand for innovative approaches to managing security and regulatory adherence in an increasingly complex technological landscape. The capital infusion is earmarked to accelerate product development, expand market reach, and further solidify Comp AI’s position as a leader in the next generation of AI-powered security and compliance platforms.
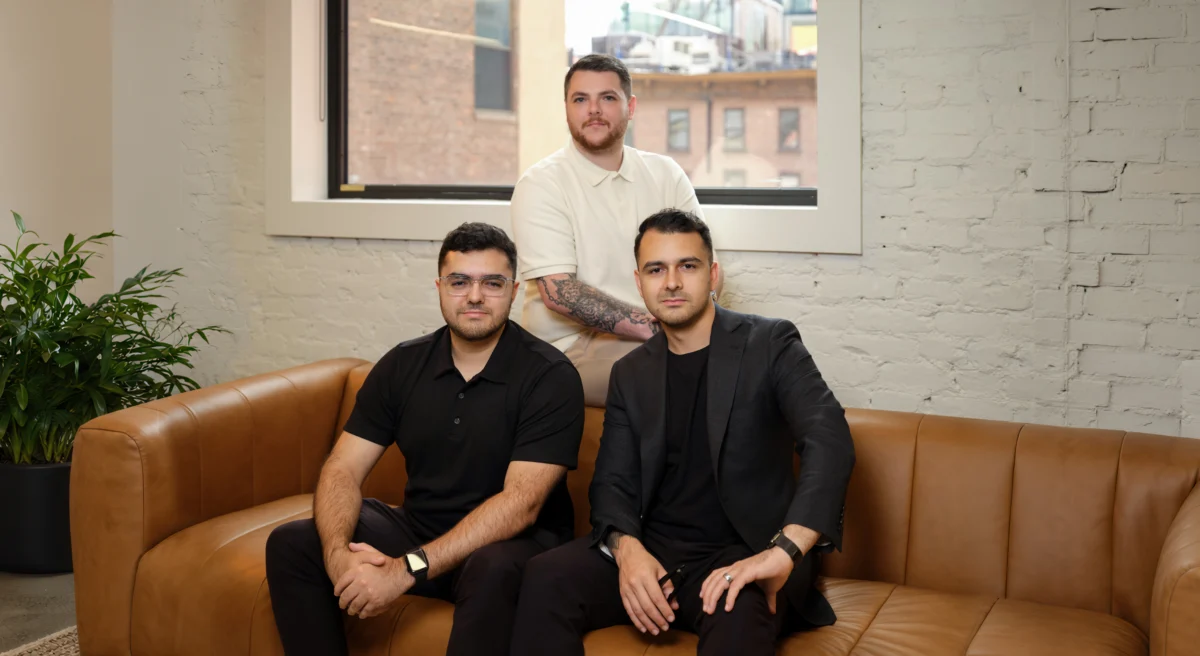
The genesis of Comp AI can be traced back to January of the previous year, founded by a trio of seasoned entrepreneurs: CEO Lewis Carhart, COO Claudio Fuentes, and CTO Mariano Fuentes. The founding team brings a wealth of experience, particularly from their prior venture, LeapAI, a workflow platform that garnered over a million users. While LeapAI ultimately ceased operations due to an inability to secure a "sticky enough use case," the experience proved invaluable. It provided critical insights into the power of Large Language Models (LLMs) and the paramount importance of identifying and catering to specific, high-value use cases. More critically, the team directly encountered the laborious and time-consuming nature of the SOC 2 compliance process, a hurdle that became increasingly apparent as they sought to scale LeapAI for larger enterprise clients.
"It’s a very obscure process," Claudio Fuentes recounted, reflecting on the challenges faced at LeapAI. "It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product." This firsthand experience with the inefficiencies and manual burdens of compliance laid the groundwork for Comp AI’s mission. The founders recognized a significant market gap for solutions that could automate and streamline these critical, yet often resource-intensive, operational tasks.
The vision for Comp AI, spearheaded by Lewis Carhart as CEO, centers on building an agentic platform designed to tackle the most tedious aspects of security and compliance. The core of their offering lies in AI agents capable of performing a range of functions, from drafting company security policies to meticulously collecting evidence required for security audits. Furthermore, the platform provides continuous monitoring to ensure that a company’s operations consistently meet defined compliance controls. This proactive and automated approach positions Comp AI as a key player in the burgeoning field of AI-driven cybersecurity, catering to businesses that are rapidly integrating AI into their operations and require robust, real-time security and compliance frameworks.
H2: Addressing the Revenue Impact of Security and Compliance
Lewis Carhart emphasized the direct correlation between robust security and compliance measures and a company’s revenue streams. "For a lot of software companies, security and compliance are directly tied to revenue," Carhart explained in an interview. He cited the common scenario where potential clients, particularly larger enterprises, require a SOC 2 report before finalizing a business deal. "What Comp AI automates is much of the work companies traditionally have to do around that process," he added. This highlights Comp AI’s strategic focus on alleviating a significant pain point that directly impacts a company’s ability to close deals and expand its customer base.
The Comp AI platform is designed to help companies meet and maintain their security requirements, but the founders are clear that it is not a replacement for independent, human-led audit reviews. Similarly, the technology is not intended to displace human workers entirely. Instead, Comp AI’s model emphasizes a symbiotic relationship between AI and human expertise. Human oversight is crucial for onboarding the AI agents, supporting the implementation of compliance controls, and maintaining the integrity of the agentic workflow.
"An agent might draft a policy, for example, but a person still reviews and approves it," Carhart elaborated. "As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly." This measured approach to AI integration, prioritizing human validation for critical decisions, reflects a mature understanding of the evolving cybersecurity landscape and the need for a balanced approach to automation.
Beyond policy generation and audit preparation, Comp AI also offers AI-powered penetration testing. This feature allows the platform to proactively test codebases and infrastructures for vulnerabilities, a critical capability in an era where new threats emerge daily. The successful Series A funding will be instrumental in expanding these capabilities and further enhancing the platform’s feature set. To date, Comp AI has raised a total of $37.5 million in funding, a testament to investor confidence in their vision and execution.
H3: The Agentic Era: New Risks and Emerging Solutions
The rapid proliferation of AI technologies across various industries has ushered in what is often termed the "agentic era." This period is characterized by the increasing deployment of autonomous or semi-autonomous AI agents that can perform complex tasks, interact with data, and influence operational workflows. While this brings immense potential for efficiency and innovation, it also introduces a new wave of security risks. This evolving threat landscape has spurred the emergence of a new generation of AI security and compliance companies, including notable players like Vanta and Drata, with Comp AI positioning itself at the vanguard of this movement.
Lewis Carhart articulated the pressing need for continuous, and potentially autonomous, security and compliance platforms in light of these developments. "Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment," he posited. "The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward." This scenario highlights a fundamental disconnect between traditional, periodic audit cycles and the dynamic nature of AI-driven operations.
Mariano Fuentes further elaborated on the challenges presented by the increasing adoption of AI. As companies deploy more intelligent agents, there is a growing requirement to meticulously track what these agents access, what actions they attempt, and whether they operate within predefined ethical and security boundaries. Comp AI is addressing this by focusing on permissions and accountability as foundational elements of its platform. "We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve," Mariano stated. This commitment to real-time monitoring and validation is crucial for maintaining trust and security in environments where AI agents are becoming increasingly integrated into core business functions.
The implications of Comp AI’s approach extend beyond mere compliance. By providing continuous visibility and control over AI agent activity, the company is enabling businesses to not only meet regulatory requirements but also to foster a culture of responsible AI deployment. This proactive stance can mitigate significant financial and reputational risks associated with data breaches, unauthorized access, and compliance failures. As AI continues its rapid integration into the fabric of business operations, the demand for sophisticated, AI-native security and compliance solutions like Comp AI is poised for substantial growth. The company’s recent funding round positions it favorably to capitalize on this trend, offering businesses the tools they need to navigate the complexities of the agentic era with confidence.