Clarissa Hana
Researchers have successfully mitigated a severe security flaw within the Time4Popcorn application, a notorious fork of the popular but legally challenged BitTorrent client Popcorn Time. This vulnerability, identified as CVE-2026-30612, allowed for the potential execution of malicious code with the highest system privileges on millions of Windows and macOS devices. The flaw stemmed from an outdated and insecure update mechanism that communicated over unencrypted HTTP and failed to validate the authenticity of executable files.
The ramifications of this discovery are significant, highlighting the persistent security risks associated with abandoned software, even when the original project has been legally shuttered or pivoted. The Time4Popcorn application, which mimicked the user-friendly interface of streaming services like Netflix to facilitate the direct consumption of BitTorrent-downloaded content, attracted a substantial user base before its own operational cessation. This widespread adoption meant that a vast number of users remained susceptible to potential exploitation long after the application’s developers ceased active maintenance.
Eye Security, the cybersecurity firm responsible for uncovering and addressing the vulnerability, took the proactive step of registering the abandoned update domain, popcorntimeupd.xyz. Their investigation revealed that this domain was still actively contacted by a significant number of Time4Popcorn clients. The firm’s telemetry indicated that up to three million Windows machines and approximately 350,000 macOS clients were still attempting to connect to this vulnerable update server. This data suggests a considerable installed base of the application, many of which appeared to be installed and forgotten, no longer actively used but still configured to seek updates.
The Anatomy of the Vulnerability
The core of the security risk lay in the application’s updater process. The Time4Popcorn updater communicated with its designated domain, popcorntimeupd.xyz, using the unencrypted HTTP protocol. This method of communication is inherently insecure, as it allows any intermediary in the network path – such as a malicious actor controlling a Wi-Fi hotspot or a compromised network device – to intercept and manipulate the data being transmitted.
More critically, the updater accepted executable files downloaded from this domain without performing any digital signature verification. Digital signatures are a crucial security mechanism that verifies the origin and integrity of software, ensuring that it has not been tampered with since it was signed by the legitimate developer. By bypassing this validation, the Time4Popcorn updater essentially trusted any executable file presented to it, regardless of its source or intent.
This combination of unencrypted communication and a lack of signature verification created a perfect storm for exploitation. An attacker who gained control of the popcorntimeupd.xyz domain could then serve malicious executables to any connected Time4Popcorn client. Because these executables were accepted without question, the attacker could execute arbitrary code on the victim’s machine with the highest possible privileges: SYSTEM on Windows and root on macOS. This level of access would allow an attacker to perform virtually any action on the compromised system, including installing malware, stealing sensitive data, enrolling the device into a botnet, or even rendering the system inoperable.

A Chronology of Discovery and Mitigation
The timeline of events leading to the remediation of this critical vulnerability is as follows:
- Pre-Discovery: The Time4Popcorn application, a fork of the original Popcorn Time, operated for a period, accumulating a significant user base. The original Popcorn Time project had been abandoned due to legal pressures surrounding copyright infringement. Forks like Time4Popcorn emerged, often continuing the distribution of content-sharing software.
- Domain Registration and Initial Analysis (Late 2025): Eye Security researchers, actively monitoring for abandoned or potentially vulnerable software infrastructure, registered the
popcorntimeupd.xyzdomain. Upon taking control of the domain, they observed a substantial volume of incoming connections from Time4Popcorn clients, indicating a widespread, albeit dormant, user base. - Vulnerability Confirmation (Early 2026): Through analysis of the update traffic and the application’s behavior, Eye Security confirmed the critical vulnerability in the updater’s communication and validation protocols. They identified CVE-2026-30612 as the specific identifier for this flaw.
- Remediation Deployment (November 2025 – March 2026): Recognizing the severe potential for abuse, Eye Security embarked on a proactive remediation campaign. Leveraging the control of the
popcorntimeupd.xyzdomain, they deployed a custom-built payload designed to disable the vulnerable updater mechanism. This operation was conducted meticulously to ensure legality and minimize user impact. The payload was specifically engineered to collect no host data or telemetry and to avoid deleting any files, thereby staying within legal boundaries. - Antivirus Evasion and Payload Refinement (Throughout Remediation): During the deployment phase, Eye Security encountered challenges with some antivirus products that flagged their legitimate remediation code as suspicious for disabling a service. This necessitated iterative refinement of their payload to ensure its successful execution without triggering undue alarms.
- Post-Remediation Monitoring and Domain Handover (March 2026 onwards): Following the successful deployment of the remediation code, Eye Security observed a dramatic decrease in update requests to their domain. By March 1, 2026, requests had dropped by an estimated 98%. Subsequently, ownership of the
popcorntimeupd.xyzdomain, along with 14 other domains historically associated with the Time4Popcorn service that Eye Security had also registered, was transferred to The Shadowserver Foundation, a non-profit organization dedicated to combating cybercrime.
Widespread User Impact and Geographic Distribution
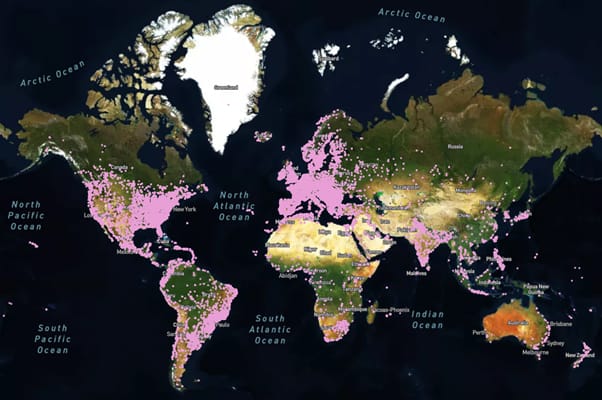
The telemetry data collected by Eye Security offered a stark illustration of the global reach of Time4Popcorn. The up to 3 million Windows and 350,000 macOS client connections originated from a diverse range of network types, including residential Internet Service Providers (ISPs), corporate networks, government facilities, and even military installations. This broad distribution underscores the pervasive nature of the threat.
The observation that most users did not appear to be actively using the app at the time of discovery is particularly noteworthy. This suggests that many users likely installed Time4Popcorn at some point in the past, perhaps for its initial convenience, and then forgot about it. The application remained installed, silently attempting to connect to its update server, thus leaving these systems perpetually vulnerable.
The geographic distribution of these users, as depicted in the accompanying map, reveals connections from a wide array of countries across North America, Europe, Asia, and South America. This global footprint meant that the potential impact of a successful exploitation could have been felt across continents, affecting individuals, businesses, and government entities worldwide.
Official Statements and Analysis
In their public disclosure, Eye Security emphasized the gravity of the situation. "If we were able to send an update, we could potentially get code execution on millions of systems," the firm stated. They further elaborated on the potential consequences: "the impact would be severe if this were to fall into the wrong hands." This statement underscores the ethical considerations that drove their proactive remediation efforts.
The decision to act preemptively, rather than simply report the vulnerability, highlights a growing trend in cybersecurity where researchers take direct action to neutralize threats when the responsible parties are unreachable or inactive. This "ethical hacking" approach, when conducted with strict adherence to legal and ethical guidelines, can be instrumental in protecting large numbers of users from imminent danger.
The transfer of the domain to The Shadowserver Foundation signifies a commitment to ongoing monitoring and, if necessary, further defensive actions should any malicious actors attempt to re-establish control over the infrastructure. Shadowserver’s mission aligns perfectly with such efforts, aiming to disrupt malicious operations and protect internet infrastructure.
Broader Implications and Remaining Risks
While Eye Security’s intervention has significantly reduced the immediate threat posed by CVE-2026-30612, the researchers caution that the risk is not entirely eliminated for all users. Two primary concerns remain:
- Android Users: The remediation strategy was primarily effective for Windows and macOS desktop clients. For Android users, the process of installing an update typically requires explicit user interaction. This manual step meant that Eye Security could not remotely disable the updater on these mobile devices. Therefore, Android users who still have Time4Popcorn installed and are prompted to update remain susceptible if a malicious actor were to gain control of the update infrastructure.
- Outdated Chrome Engine: The Time4Popcorn application incorporates a significantly outdated Chrome engine, dating back to 2014. This version of the browser engine lacks modern security features, including robust sandbox protections. Sandboxing is a critical security mechanism that isolates processes, preventing them from accessing or affecting other parts of the system. Without these protections, vulnerabilities within the Chrome engine itself could be exploited by attackers to gain unauthorized access and execute malicious code, even if the updater mechanism is no longer a direct vector.
The most effective course of action for any user who still has Time4Popcorn installed on their systems, regardless of operating system, is to completely remove the software. This measure eliminates the attack surface entirely, safeguarding against both the known updater vulnerability and any potential exploits targeting the outdated browser engine.
The incident serves as a potent reminder of the long-term security implications of using software that is no longer actively maintained or updated by its developers. Users often remain unaware of the vulnerabilities lurking in abandoned applications, creating a fertile ground for cybercriminals. The proactive and responsible actions of Eye Security have undoubtedly prevented a widespread security incident, but they also highlight the ongoing need for user vigilance and the importance of uninstalling outdated and unsupported software. The potential for a botnet of millions, as envisioned by the researchers, has been averted, but the threat landscape is ever-evolving, and similar vulnerabilities may lie dormant in other forgotten applications.