Chandra Wibowo
Ledger, a prominent hardware cryptocurrency wallet manufacturer, has been compelled to suspend its reseller network across Southeast Asia and Hong Kong following a sophisticated supply chain attack that resulted in the theft of over $103.4 million from 530 compromised addresses. The attack involved tampered Ledger devices being inserted into the supply chain, allowing thieves to install spyware capable of recording users’ seed phrases. In a twist of fate that has garnered significant attention within the cryptocurrency community, one of the individuals who fell victim to this elaborate scheme was reportedly a scammer themselves, as detailed by blockchain analytics firm Chainalysis.
This individual, who allegedly operated a "task scam" that preyed on individuals by offering payment for fake sales and reviews, lost approximately $4.8 million worth of Bitcoin from three newly purchased Ledger devices. These devices, according to Chainalysis, contained the malicious spyware that captured the scammer’s seed phrases. The thieves then systematically drained all three of the compromised wallets into a single destination wallet, highlighting a level of precision and coordination in the attack. The irony is compounded by the nature of the scammer’s own operation, which often involved participants being coerced into depositing their own funds to "resolve negative balances" before payment. This scenario has led to speculation that the victim may have been a "scammer of scammers," illustrating the complex and often opaque layers of illicit activity within the digital asset space.
The incident has sent ripples of concern through the hardware wallet sector, prompting Ledger to take decisive action. The company has formally requested its resellers in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong to immediately halt sales of its devices. This measure is intended to prevent further compromised devices from reaching consumers and to allow for a thorough investigation into the breach. While Ledger has confirmed the confirmed thefts to date are concentrated in Asia, reports have also emerged of tampered Ledger devices appearing in Europe. This led to electronics retailer MediaMarkt suspending sales of the devices in that region, underscoring the potential global reach of the supply chain vulnerability.
In a preemptive move to bolster its own security posture, rival hardware wallet manufacturer Trezor has also announced it will be discontinuing sales through some of its more distant resellers starting January 1. This decision stems from Trezor’s inability to guarantee the same level of vigilance over its supply chain as it can with resellers located closer to its operational hubs. While Trezor has taken these steps, there have been no reports of tampered Trezor devices being involved in any thefts.
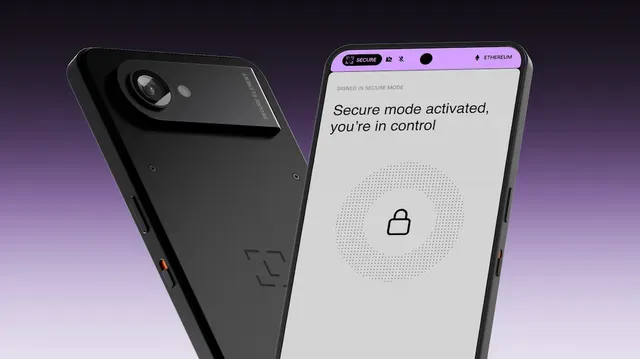
This hardware wallet scandal is being compared to the Coldcard seed phrase debacle that occurred at the end of July, another incident that raised serious questions about the security of cryptocurrency storage solutions. Amidst this challenging period, Ledger has chosen to launch its latest device, the Ledger Atom. Priced at $849, the Atom is designed to integrate a cryptocurrency wallet with Android applications, with a key feature being the strict separation of these applications from sensitive wallet operations. Ledger claims that the Atom incorporates advanced protections specifically engineered to counter the type of implants used in the Asian thefts, asserting that its tamper-detection capabilities are effective even when the device is switched off.
Genesis of the Ledger Supply Chain Attack: A Timeline of Deception
The sophisticated nature of the Ledger supply chain attack suggests a meticulously planned operation. While precise timelines for the inception of the attack remain under investigation, the impact became evident in recent weeks as reports of stolen funds began to surface.
- Pre-Attack Phase: The attackers likely identified a vulnerability within Ledger’s distribution network. This could have involved compromising third-party logistics providers, manufacturing partners, or even corrupting individuals within the reseller channels. The goal would have been to gain unauthorized access to devices before they reached end-users.
- Device Tampering: Once access was gained, the attackers would have introduced malicious hardware or software into the Ledger devices. This likely involved implanting spyware designed to intercept and record the user’s recovery seed phrase during the initial setup process. The seed phrase is the master key to a user’s cryptocurrency holdings, making its compromise catastrophic.
- Distribution and Compromise: The tampered devices were then reintroduced into the supply chain and distributed through various resellers across Southeast Asia. Unsuspecting customers purchased these devices, believing them to be secure and legitimate. During the setup of these compromised devices, the spyware would have activated, capturing the user’s seed phrase.
- Fund Extraction: After obtaining the seed phrases, the attackers would have been able to remotely access and drain the cryptocurrency holdings from the affected wallets. The reported figure of over $103.4 million stolen from 530 addresses indicates a significant volume of assets targeted.
- Discovery and Response: As victims began to report losses, blockchain analytics firms like Chainalysis and security researchers started to investigate. The pattern of compromised devices and stolen funds quickly pointed towards a supply chain attack. Ledger’s swift response included suspending sales in affected regions and issuing advisories to its customer base.
The Scammer’s Downfall: A Poetic Twist of Digital Justice
The identification of a scammer as one of the victims adds a layer of intrigue to an already concerning incident. Chainalysis reported that the scammer lost 60 Bitcoin, a substantial sum valued at approximately $4.8 million at the time of the report. The fact that the scammer’s stolen funds were consolidated into a single wallet, and that this wallet was associated with the tampered Ledger devices, provides strong evidence of their direct victimization.
This particular scammer’s modus operandi, described as a "task scam," involved recruiting individuals to perform seemingly simple tasks, such as leaving fake reviews or engaging in simulated online sales. Participants were initially compensated, but the scam would often escalate, with victims being informed of a "negative balance" and pressured to deposit their own funds to receive payment. This circular and exploitative model highlights a disturbing trend in online fraud.
The irony of this scammer falling victim to another, arguably more sophisticated, form of digital deception is not lost on observers. It serves as a stark reminder that even those who engage in fraudulent activities are not immune to becoming targets themselves. The interconnected nature of the digital world means that vulnerabilities can be exploited at any level, and the lines between perpetrator and victim can become blurred. This instance raises questions about the ethical implications of profiting from scams and the potential for retribution, however accidental, within the digital underground.
Broader Implications for Hardware Wallet Security and the Crypto Market
The Ledger supply chain attack has significant implications for the broader cryptocurrency market and the trust users place in hardware wallets. These devices are considered the gold standard for secure offline storage of digital assets, offering a critical layer of protection against online threats. A breach of this magnitude, affecting a leading manufacturer, can erode user confidence and potentially lead to a reassessment of security protocols across the industry.
Increased Scrutiny of Supply Chains: This incident will undoubtedly lead to increased scrutiny of the entire supply chain for hardware wallets and other sensitive electronic devices. Manufacturers will need to implement more robust verification processes, conduct deeper due diligence on third-party partners, and explore advanced anti-tampering technologies throughout the manufacturing and distribution phases.
Regulatory Pressure: Regulators worldwide are already grappling with how to oversee the burgeoning cryptocurrency industry. A major security incident like this could accelerate calls for stricter regulations and compliance standards for hardware wallet manufacturers and crypto service providers. This could include mandated security audits, enhanced traceability requirements, and more stringent penalties for security breaches.
Consumer Education and Due Diligence: While hardware wallets remain a crucial security tool, this event underscores the importance of consumer education. Users need to be aware of the risks associated with purchasing devices from unofficial or unauthorized resellers. The practice of buying second-hand hardware wallets or those from untrusted sources should be strongly discouraged. Furthermore, users should be vigilant in verifying the authenticity of their devices and understanding the setup procedures to identify any anomalies.
Impact on Ledger’s Reputation: Ledger, a company that has built its brand on the promise of unparalleled security, now faces the challenge of rebuilding trust. While their swift response and transparency in acknowledging the issue are positive steps, the long-term impact on their market position will depend on their ability to effectively address the vulnerabilities and implement lasting security enhancements.
Competitive Landscape: The incident could also create opportunities for competitors. As users seek alternative solutions, other hardware wallet manufacturers and even software wallet providers may see an increase in demand. This could lead to a more dynamic and potentially more secure competitive landscape as companies strive to differentiate themselves on the basis of their security track record.
Regional Developments and the Evolving Crypto Landscape
Beyond the Ledger incident, several other significant developments are shaping the cryptocurrency landscape across Asia and beyond:
South Korea’s Regulatory Push: South Korean authorities are taking a proactive stance against unregistered crypto exchanges. The approval to block access to 27 overseas crypto exchange websites, including major platforms like KuCoin and MEXC, demonstrates a commitment to protecting domestic users from illicit operators. This move follows a broader cybersecurity overhaul initiated after attacks impacted both traditional banks and crypto firms in the country, highlighting a growing awareness of digital asset security risks. In a separate development, Jeonbuk Bank has reportedly begun offering Bitcoin-backed business loans, indicating a cautious but evolving integration of cryptocurrencies into traditional financial services in South Korea.
Thailand’s ETF Debut: Thailand has finalized rules allowing for the listing of crypto exchange-traded funds (ETFs) on its main stock exchange. Initially focusing on Bitcoin and Ether ETFs, the market is expected to see modest inflows, with experts anticipating tens of millions of US dollars rather than billions in the early stages. The regulations are designed to favor domestic products, with restrictions on investments in overseas crypto ETFs for most individuals.
Australia’s Regulatory Framework: Australia is actively seeking public feedback on proposed capital, custody, and trading requirements for crypto platforms, with legislation slated for rollout by 2027. The Australian Securities and Investments Commission (ASIC) is considering various capital models, restrictions on proprietary trading by platforms, and quarterly reporting for customer asset wallets. The regulator is also exploring the extension of rules governing Contracts for Difference (CFDs) to crypto assets.
China’s Legal Setback for Fraud Victims: In China, victims of a massive Bitcoin fraud have lost a significant legal battle in London. The High Court ruled that Chinese law, rather than English law, should govern claims to approximately 61,000 Bitcoin seized by the British government. This decision stems from an investment fraud scheme orchestrated between 2014 and 2017, and the claimants are reportedly planning to appeal the ruling.
Philippines’ Exchange License Uncertainty: Coins.ph, a major crypto exchange in the Philippines, has asserted that its license from the country’s central bank remains intact, despite reports of potential revocation. The exchange denies knowingly facilitating transactions with offshore gambling operators, a concern that has prompted restrictions on certain incoming transfers.
Hong Kong’s Growing ETF Market and Exchange Offerings: Hong Kong continues to expand its digital asset offerings. Binance co-CEO Richard Teng indicated the exchange may add Asian equities, including those from Hong Kong, Korea, Taiwan, and Brazil, to its platform. Furthermore, Pando Finance has launched its Solana ETF on the Hong Kong Stock Exchange (HKEX), marking the second such fund and offering a lower fee structure compared to its predecessor.
Singapore’s Declining Scam Losses and Expansion Plans: Singapore has reported a significant 43% year-over-year decrease in reported losses from crypto scams, attributed in part to a crackdown by the police in collaboration with local crypto exchanges. In a move signaling its commitment to the region, Revolut has announced plans to open a new Singapore office, invest substantial capital, and expand its local workforce.
The Ledger supply chain attack serves as a stark reminder of the persistent threats within the cryptocurrency ecosystem. While the industry continues to innovate and expand, the fundamental importance of robust security measures, transparent supply chains, and vigilant user practices cannot be overstated. The ironic downfall of a scammer amidst this crisis only adds another layer to the complex narrative of digital finance and the perpetual cat-and-mouse game between fraudsters and those seeking to protect their assets.