Clarissa Hana
Researchers at Eye Security have successfully remediated a critical remote code execution (RCE) vulnerability within the updater of Time4Popcorn, a popular but now abandoned fork of the notorious BitTorrent client Popcorn Time. The flaw, identified as CVE-2026-30612, left millions of Windows and macOS users susceptible to having malicious code executed on their systems with elevated privileges. The security firm proactively registered the application’s abandoned update domain, popcorntimeupd.xyz, and leveraged the vulnerability to deploy a benign payload that disabled the updater, effectively neutralizing the threat for a vast number of users.
The vulnerability stemmed from the Time4Popcorn updater’s insecure communication protocols and lax verification of update files. The updater contacted its designated domain, popcorntimeupd.xyz, exclusively over unencrypted HTTP. Crucially, it accepted any executable file presented as an update without performing digital signature verification. This fundamental flaw meant that any entity gaining control of the popcorntimeupd.xyz domain could intercept and manipulate the update traffic. By serving a malicious executable, an attacker could have achieved code execution with the highest privileges on targeted systems: SYSTEM on Windows and root on macOS. This level of access would grant an attacker complete control over a compromised machine, allowing them to steal data, install further malware, or enlist the device into a botnet.
Background of Popcorn Time and its Forks
Popcorn Time, initially launched in 2014, gained notoriety for its user-friendly, Netflix-style interface that seamlessly integrated BitTorrent downloading with media playback. This facilitated the consumption of copyrighted content, leading to its rapid downfall due to legal pressures and copyright infringement concerns. The original project was ultimately abandoned by its developers. However, the concept proved popular, spawning numerous forks and derivative applications that continued to operate under the Popcorn Time banner. Time4Popcorn emerged as one such prominent fork, attracting a significant user base by offering a similar streaming experience, albeit often through unofficial channels and without clear legal standing. The longevity of these forks, even after the original project’s demise, highlights the demand for accessible media streaming solutions, even those operating in legal grey areas.
The Discovery and Scale of the Threat
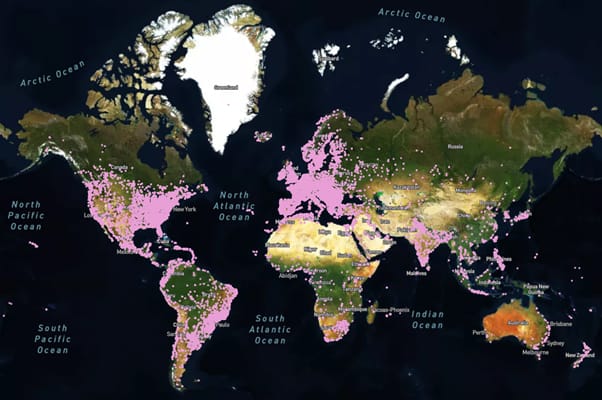
The security risk was brought to light by researchers at Eye Security, who stumbled upon the vulnerability during routine domain monitoring. Recognizing the potential for abuse, they registered the abandoned popcorntimeupd.xyz domain. Upon observing network traffic, they discovered a substantial number of client connections to the Time4Popcorn updater. Their telemetry indicated that up to 3 million Windows clients and approximately 350,000 macOS clients were still attempting to connect to the outdated update server. This staggering number underscored the widespread reach of the Time4Popcorn application and the magnitude of the potential security breach.
Further analysis of the connection data revealed that these clients were predominantly originating from residential internet service providers (ISPs), as well as corporate, government, and even military networks. Intriguingly, the researchers noted that the majority of these users did not appear to be actively engaging with the Time4Popcorn application at the time of the connections. This suggests that many users had installed the software in the past and subsequently forgotten about it, leaving their systems vulnerable to exploitation without their knowledge. The sheer volume of these "dormant" installations presented a significant, albeit passive, threat landscape.
"If we were able to send an update, we could potentially get code execution on millions of systems," Eye Security stated in their report detailing the operation, emphasizing the severe consequences had the vulnerability been exploited by malicious actors. "The impact would be severe if this were to fall into the wrong hands." The discovery and subsequent remediation effort highlight a critical aspect of cybersecurity: the ongoing risks posed by abandoned software that continues to be installed and operate on user devices.
Chronology of the Remediation Operation
The remediation effort undertaken by Eye Security was meticulously planned and executed between November 2025 and March 2026. The researchers strategically leveraged the very vulnerability they had discovered to deliver a benign remediation payload. This payload was designed to interact with the Time4Popcorn updater through the compromised popcorntimeupd.xyz domain and effectively disable the updater mechanism.

The researchers understood the delicate legal and ethical considerations involved in such an operation. To ensure their actions remained within a fully legal context and to avoid any accusations of unauthorized access or data compromise, the payload was deliberately designed to be non-intrusive. It collected no host data or telemetry and did not delete any files on users’ computers. Its sole purpose was to neutralize the security risk by stopping and disabling the vulnerable updater.
During the testing phase of the remediation payload, Eye Security encountered an unexpected challenge: some antivirus products flagged their legitimate disabling code as malicious. This necessitated modifications to the payload to ensure it could effectively perform its intended function without being erroneously quarantined or blocked by security software. This aspect of the operation underscores the complexities of cybersecurity interventions, where legitimate security actions can sometimes be misinterpreted by automated security systems.
Following the deployment of the remediation code, Eye Security observed a significant decrease in malicious update requests. They recorded approximately 2 million successful update downloads, indicating the reach of their intervention. By March 1, 2026, requests to their controlled update domain had plummeted by an impressive 98%, a clear indicator of the operation’s success in neutralizing the threat.
Upon the successful completion of the remediation operation, Eye Security took the crucial step of transferring ownership of the popcorntimeupd.xyz domain to The Shadowserver Foundation. Shadowserver is a non-profit organization dedicated to helping reduce and prevent security threats worldwide, making them an ideal steward for the domain, ensuring its continued use for defensive purposes and ongoing monitoring.
Broader Implications and Remaining Risks
Despite the significant success of Operation Ixim, the researchers cautioned that the threat is not entirely eliminated for all users of the Time4Popcorn application. Two primary areas of concern remain:
-
Android User Exposure: The remediation efforts were largely focused on Windows and macOS desktop clients. For Android users, the situation is more complex. Installing an update on mobile devices typically requires explicit user interaction. Consequently, remotely disabling the updater for Android clients through the same mechanism used for desktop versions was not feasible. This means Android users who still have Time4Popcorn installed may remain vulnerable if a malicious actor were to gain control of the update infrastructure and trick users into manually accepting a malicious update.
-
Outdated Chrome Engine Vulnerabilities: A fundamental security weakness within the Time4Popcorn application itself persists. The app relies on a severely outdated version of the Chrome browser engine, reportedly from 2014. This ancient engine lacks modern sandboxing protections and is likely riddled with numerous known and exploitable vulnerabilities. Even if the updater is disabled, the outdated browser engine could be a primary target for attackers seeking to compromise user systems. Exploiting such a legacy component could provide a direct entry point into the user’s device, bypassing the now-secured updater mechanism.
Given these persistent risks, Eye Security strongly advises users to uninstall the Time4Popcorn application entirely from their systems. This is the most effective and definitive way to mitigate any remaining security threats associated with the software. The incident serves as a stark reminder of the importance of regularly reviewing installed software, uninstalling applications that are no longer used, and staying vigilant about software updates, especially from less reputable sources.
Analysis of the Vulnerability and Remediation Strategy
The vulnerability CVE-2026-30612 exemplifies a common, yet critical, security oversight: the reliance on unencrypted communication for updates and the failure to validate the integrity of update files. In an era where data interception and man-in-the-middle attacks are prevalent, transmitting sensitive information like software updates over plain HTTP is a significant security lapse. The lack of digital signature verification is equally problematic, as it allows for the seamless injection of arbitrary code disguised as legitimate updates.
Eye Security’s proactive approach to registering the abandoned domain and then using the vulnerability for remediation is a notable example of "white-hat" hacking. This strategy, often referred to as "hack-back" or "ethical hacking" in a defensive context, allows security researchers to neutralize threats that could otherwise be exploited by malicious actors. However, it requires careful planning, precise execution, and a clear understanding of legal and ethical boundaries to avoid unintended consequences. The researchers’ commitment to a non-intrusive payload and their transparency in reporting the operation are crucial elements that lend credibility to their actions.
The success of their remediation, evidenced by the dramatic drop in update requests, demonstrates the effectiveness of targeted interventions against abandoned software. However, the persistence of the Android vulnerability and the outdated browser engine underscores that even successful remediation efforts may not completely eliminate risk. This situation highlights the broader challenge of managing the security of legacy software and the responsibility of users to maintain secure computing environments.
Supporting Data and Context
The incident involving Time4Popcorn’s updater adds to a growing body of evidence highlighting the persistent security risks posed by outdated and abandoned software. A recent report by a leading cybersecurity firm indicated that a significant percentage of enterprise networks still harbor legacy applications with known vulnerabilities, often due to compatibility issues or lack of viable replacement options. The Time4Popcorn case, while focused on consumer software, illustrates a similar underlying problem: software that is no longer actively maintained or supported becomes a prime target for exploitation.
The estimated number of affected users—up to 3 million on Windows and 350,000 on macOS—places this vulnerability in the category of a widespread threat. The fact that these connections were observed suggests that many users were unaware of the inherent risks. This lack of user awareness is a recurring theme in cybersecurity, where sophisticated technical vulnerabilities can have a devastating impact due to simple oversight.
The researchers’ decision to transfer the domain to The Shadowserver Foundation is a best practice in cybersecurity incident response. By entrusting the domain to a reputable security organization, they ensure that it can continue to serve a defensive purpose, potentially by blocking malicious traffic or by being used for further research into similar threats.
Looking Ahead
The Time4Popcorn incident serves as a critical case study for both users and software developers. For users, it underscores the importance of uninstalling unused software, especially applications that may operate in legally ambiguous areas or are no longer supported. The convenience of streaming applications, while appealing, must be balanced against the potential security risks.
For software developers and security researchers, this event reinforces the need for proactive vulnerability management, even for projects that have been officially abandoned. The discovery of such critical flaws in long-dormant software highlights the ongoing challenge of securing the digital ecosystem against threats that can emerge from unexpected quarters. The successful remediation by Eye Security offers a blueprint for how such threats can be addressed, but it also emphasizes that vigilance and continuous monitoring remain paramount in the ever-evolving landscape of cybersecurity. The best defense, as always, begins with awareness and responsible digital hygiene.