Clarissa Hana
A new, highly organized malware campaign is leveraging Search Engine Optimization (SEO) tactics on GitHub to impersonate legitimate software companies and distribute a previously unknown information-stealing malware dubbed "Rapuncel." The operation, uncovered by cybersecurity firms LastPass and Delphos Labs, also deploys a Microsoft-signed kernel driver capable of disabling a staggering 145 different antivirus and endpoint detection and response (EDR) products, posing a significant threat to user security and corporate defenses.
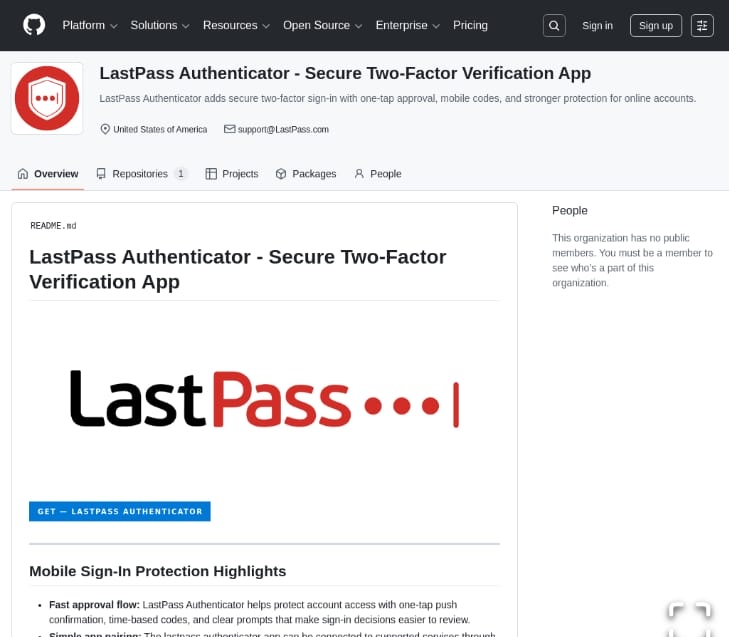
The intricate attack chain begins with victims actively searching for popular software, such as the LastPass Authenticator, or other well-known applications. Cybercriminals have meticulously crafted GitHub repositories, optimizing them with relevant keywords to rank highly in search engine results. This deceptive strategy leads unsuspecting users to these malicious repositories, which are designed to mimic the official presence of established software vendors. Once on a compromised page, users are enticed by seemingly legitimate "download" buttons. However, clicking these buttons initiates a complex series of redirects, ultimately leading to payload-delivery servers controlled by the attackers.
These servers then provide victims with seemingly innocuous ZIP archives. To circumvent initial security scans and detection mechanisms, these archives have their file sizes artificially inflated, reaching up to a substantial 148 megabytes. Upon extraction, users discover an installer that masquerades as a legitimate Microsoft component: the Visual Studio CoreCLR Debugger, ‘vsdbg.exe.’ This installer has been ingeniously modified to sideload a malicious Dynamic Link Library (DLL) named ‘vsdbg.dll.’ This malicious DLL is the primary conduit for deploying both the Rapuncel infostealer and a critical kernel driver, identified as Alinubx.sys.
The Alinubx.sys Kernel Driver: A Potent EDR Killer
The Alinubx.sys driver is the cornerstone of the campaign’s ability to evade detection. It is cleverly disguised as a legitimate NVIDIA component, specifically named ‘nvfsflt64.sys,’ and registers itself within the operating system as the ‘NvFsFilter’ service. This camouflage is crucial for its malicious purpose: to act as a sophisticated EDR killer. Researchers at LastPass and Delphos Labs have identified that this driver contains a hardcoded list of 145 distinct antivirus and EDR processes that it actively seeks to terminate.
The mechanism by which Alinubx.sys achieves this is particularly concerning. According to LastPass’s technical analysis, the driver utilizes a low-level kernel function, ‘ObOpenObjectByPointer,’ with ‘AccessMode=KernelMode.’ This specific invocation allows the driver to bypass the standard user-mode security checks that would normally prevent unauthorized access to critical system processes. By directly interacting with the kernel, the driver can request access to processes as kernel code, effectively disabling the security protections that many antivirus and EDR solutions rely upon, including Protected Process Light (PPL). PPL is a security feature designed to prevent even administrator-level users from tampering with critical security processes, making the driver’s ability to bypass it a significant threat.
Adding to the concern is the fact that the Alinubx.sys driver, as deployed in this campaign, is digitally signed. This signature originates from Microsoft’s Windows Hardware Compatibility Publisher chain. While not inherently malicious, a legitimate signature lends an air of trustworthiness to the driver, potentially allowing it to pass through some security checks that would flag unsigned or improperly signed kernel-mode drivers. Crucially, at the time of discovery, this specific driver was not present on Microsoft’s vulnerable driver blocklist, a list that tracks known malicious or exploitable drivers.
While the primary function of Alinubx.sys in this campaign is to disable security software, researchers have noted that the driver possesses a broader, more sinister set of capabilities that are not currently activated. These include advanced functions for hiding files and registry entries, injecting DLLs into other processes, intercepting driver and process activities, manipulating network traffic, and redirecting network ports. The potential for these dormant features to be activated in future iterations of the campaign raises the stakes considerably.
The Rapuncel Infostealer: A Data Harvesting Machine
Once the Alinubx.sys driver has successfully neutralized all forms of active security protection on a compromised device, the Rapuncel infostealer commences its data-gathering operations. This malware is designed to meticulously exfiltrate a wide range of sensitive information from the infected system. While the original report did not detail the specific types of data collected by Rapuncel, such information-stealers typically target credentials (usernames and passwords), financial information (credit card details, banking credentials), personal identification data, browser history, cookies, and system configuration details. The goal is to gather enough information to facilitate identity theft, financial fraud, or to gain further access to corporate networks.
A particularly noteworthy aspect of Rapuncel’s operation is its method for bypassing advanced security measures employed by modern web browsers. To circumvent Google’s app-bound encryption protection, which is a security feature present in Chrome, Edge, and other Chromium-based browsers, Rapuncel injects a specialized helper DLL into the browser’s process. It then invokes its own "Elevation Service," a technique that allows it to elevate its privileges and gain the necessary access to steal encrypted data.
The exfiltrated data is then compressed by Rapuncel before being transmitted to an external command-and-control (C2) server. The report indicates that this data is sent using an HTTP-formatted request, specifically over raw TCP, to the IP address <kbd>2.26.126[.]50</kbd>. This direct communication method, bypassing standard HTTP libraries, can sometimes be used to evade network intrusion detection systems that primarily monitor conventional web traffic.
To ensure its persistence across system reboots, Rapuncel establishes itself as a Windows service. This means that even if a system is restarted and any reactivated security tools attempt to scan for threats, Rapuncel’s persistence mechanism ensures that the Alinubx.sys driver is launched again to terminate them before the infostealer can be detected and removed.
Attribution and Technical Analysis
LastPass and Delphos Labs have assessed with moderate confidence that Rapuncel is a variant of the BoryptGrab infostealer. This suggests a potential connection to existing threat actor groups or a lineage of malware development. Furthermore, the loader component of the malware was found to be built using the Cruciferra PUROSANGUE crypter. Crypters are tools used by malware authors to obfuscate their malicious code, making it more difficult for antivirus software to detect. The use of a specific crypter like Cruciferra PUROSANGUE can sometimes provide clues about the technical sophistication and resources of the threat actor.
The Evolving Threat Landscape and Mitigation Strategies
This campaign highlights a concerning evolution in cybercriminal tactics. The sophisticated use of SEO to manipulate search results, the creation of highly convincing fake repositories on a trusted platform like GitHub, and the deployment of a powerful, kernel-mode antivirus-bypassing driver demonstrate a significant level of planning and technical expertise. The fact that the malicious driver is Microsoft-signed and bypasses PPL protections underscores the challenges faced by even the most advanced security solutions.
The implications of such a campaign are far-reaching. For individuals, the compromise of credentials and personal data can lead to identity theft, financial ruin, and reputational damage. For organizations, the successful deployment of Rapuncel and its associated driver can result in the theft of sensitive corporate data, intellectual property, and the disruption of business operations. The ability of the driver to disable multiple EDR solutions means that even well-protected corporate networks could be vulnerable if an employee falls victim to this phishing-like attack.
In response to this threat, cybersecurity experts offer several key recommendations:
- Download Software Only from Official Sources: Users should exercise extreme caution and only download software directly from the official websites of the developers or trusted application stores. Avoid clicking on links from search results that seem too good to be true or originate from unfamiliar sources.
- Be Wary of GitHub Repositories: While GitHub is a valuable platform for developers, it can also be exploited by malicious actors. Users should be skeptical of software downloads from GitHub, especially if the repository lacks a clear history, extensive documentation, or official endorsements.
- Exercise Caution with Search Engine Results: Promoted or sponsored results on search engines, particularly for software downloads, should be approached with extreme caution. Attackers often pay to have their malicious links appear at the top of search results.
- Maintain Up-to-Date Security Software: While this campaign has demonstrated a method to bypass many AV/EDR solutions, keeping all security software updated is still a fundamental layer of defense. Updates often include signatures and behavioral analysis techniques that can detect emerging threats.
- Enable Multi-Factor Authentication (MFA): For critical online accounts, especially those related to password managers, email, and financial services, enabling MFA provides an essential additional layer of security, even if credentials are compromised.
- Educate Users: Continuous user education on cybersecurity best practices, phishing awareness, and the risks associated with downloading software from untrusted sources remains a crucial element in preventing such attacks.
The ongoing investigation into the Rapuncel campaign by LastPass and Delphos Labs serves as a stark reminder of the persistent and evolving nature of cyber threats. The sophisticated tactics employed by these threat actors necessitate a proactive and informed approach to cybersecurity for both individuals and organizations alike. The race between attackers developing new evasion techniques and defenders creating robust detection and prevention mechanisms continues, underscoring the critical importance of vigilance and continuous adaptation in the digital realm.