Clarissa Hana
Researchers have successfully neutralized a significant security vulnerability within the abandoned Time4Popcorn application, a derivative of the popular BitTorrent client Popcorn Time. This critical flaw, identified as CVE-2026-30612, allowed for remote code execution (RCE) with elevated privileges on potentially millions of Windows and macOS devices. The vulnerability stemmed from an insecure updater mechanism that communicated over unencrypted HTTP and failed to validate digital signatures of downloaded executables, leaving users susceptible to malicious takeovers.
The Genesis of the Vulnerability: A Forked Path and Digital Neglect
The Popcorn Time application initially gained notoriety for its Netflix-style interface that seamlessly integrated BitTorrent downloads, enabling users to stream pirated content directly within the application. Facing legal repercussions, the original project was officially abandoned. However, its widespread appeal led to the emergence of numerous forks, with Time4Popcorn being one of the most prominent to resurface under the Popcorn Time banner. These forks, often maintained by independent developers or left unattended, quickly amassed millions of users who were drawn to the familiar interface and perceived convenience, often unaware of the evolving security landscape surrounding these applications.
The core of the discovered vulnerability lay in the updater component of Time4Popcorn. This updater, responsible for delivering software updates, contacted an abandoned domain, popcorntimeupd.xyz. Crucially, this communication occurred over plain HTTP, a protocol that transmits data in an easily interceptable and modifiable format. Furthermore, the updater lacked any mechanism to verify the authenticity of the executables it downloaded. This meant that any entity gaining control of the popcorntimeupd.xyz domain could intercept the traffic, replace legitimate update files with malicious ones, and subsequently execute arbitrary code on users’ machines. For Windows users, this translated to the potential for code execution with SYSTEM privileges, the highest level of authority on the operating system. On macOS, attackers could achieve root privileges, similarly granting them complete control over the system.
Discovery and the Scale of the Threat: Eye Security’s Intervention
The critical security risk was brought to light by researchers at Eye Security. Their investigation began when they registered the dormant popcorntimeupd.xyz domain. Upon monitoring traffic directed to this domain, they were astonished by the sheer volume of connections. Their analysis revealed that up to an estimated 3 million Windows clients and 350,000 macOS clients were attempting to contact the Time4Popcorn updater. This staggering number underscored the widespread reach of the vulnerable application.
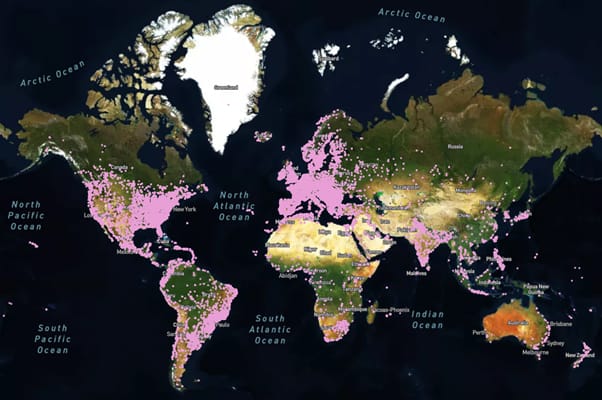
Further analysis of the connection data, including an illustrative map showcasing user locations, revealed that these connections originated from a diverse range of networks. This included residential internet service providers (ISPs), corporate networks, government agencies, and even military installations. The geographical distribution indicated a global user base, amplifying the potential impact of any successful exploitation.
Interestingly, the researchers observed that a significant portion of these users did not appear to be actively engaging with the Time4Popcorn application at the time of their connections. This observation led to the hypothesis that many of these installations were likely from a period when the app was more actively used, and the software had subsequently been installed and then largely forgotten by its users. This "set it and forget it" mentality among a large user base created a fertile ground for exploitation, as these individuals would be unlikely to notice or respond to any signs of compromise.

"If we were able to send an update, we could potentially get code execution on millions of systems," stated Eye Security in their detailed report, emphasizing the severity of the situation. They further elaborated, "the impact would be severe if this were to fall into the wrong hands." This statement highlights the dual nature of the discovery: a significant threat to a vast number of users, but also an opportunity for responsible actors to mitigate the risk.
A Proactive Remediation: Operation Ixim
Recognizing the immediate and substantial threat, Eye Security embarked on a proactive remediation effort, which they dubbed "Operation Ixim." This operation was designed to disable the vulnerable updater mechanism without compromising user data or systems. Between November 2025 and March 2026, the researchers leveraged the very vulnerability they had discovered to deliver a "remediation code." This code was specifically designed to identify and disable the Time4Popcorn updater service on affected machines.
A key principle guiding Eye Security’s intervention was adherence to legal and ethical boundaries. Their remediation payload was meticulously crafted to avoid collecting any host data or telemetry. It did not delete any files on users’ computers, ensuring that their actions remained strictly within a legal context and focused solely on neutralizing the security risk. This approach underscored their commitment to responsible disclosure and ethical hacking.
During the development and testing phases of the remediation payload, the researchers encountered a common challenge in cybersecurity: antivirus software. Some antivirus products flagged their code for disabling a service, a function that can be indicative of malicious activity. Eye Security had to adapt and modify their payload to effectively bypass these detection mechanisms while still achieving their objective of disabling the updater. This iterative process highlights the complexities of security interventions and the constant cat-and-mouse game between security researchers and defensive systems.
The impact of Operation Ixim was demonstrably successful. Following the deployment of the remediation code, Eye Security recorded approximately 2 million update downloads, indicating the reach of their efforts. By March 1, 2026, requests to their controlled update domain had plummeted by an astonishing 98%, a clear indicator that the vulnerable updater had been effectively neutralized for the vast majority of its previous user base.
Transitioning to Long-Term Security and Remaining Concerns
Upon the successful completion of the remediation operation, Eye Security took the crucial step of transferring ownership of the popcorntimeupd.xyz domain, along with 14 other associated domains they had registered, to the non-profit security organization The Shadowserver Foundation. This handover ensures that these domains will be managed responsibly and continue to serve as a deterrent against future exploitation attempts by malicious actors. The Shadowserver Foundation is well-known for its work in tracking and mitigating botnets and other cyber threats, making them an ideal steward for these domains.
Despite this significant success in mitigating the remote code execution threat for Windows and macOS users, the researchers have cautioned that the risk is not entirely eliminated. Several factors continue to pose potential threats to a segment of Time4Popcorn users.
Firstly, Android users of the Time4Popcorn application remain exposed. The mechanism for updating applications on Android often requires explicit user interaction for installation. This means that the remote disabling of the updater, as was possible on desktop operating systems, could not be directly applied to the mobile platform without user consent. Consequently, attackers could potentially still exploit the vulnerability on Android devices if they could trick users into installing a malicious update.
Secondly, a deeper concern lies within the core Time4Popcorn application itself. The application’s integrated Chrome engine is severely outdated, reportedly stemming from a 2014 version. Modern web browsers incorporate numerous security features, including sandboxing, which isolates web content and prevents malicious code from escaping into the operating system. The absence of these crucial sandbox protections in the 2014 Chrome engine presents a significant attack surface. Even if the updater vulnerability were fully patched, attackers could potentially exploit inherent weaknesses within the outdated browser component to achieve code execution.
Given these persistent risks, the most prudent recommendation for users who still have Time4Popcorn installed on their systems is to uninstall the software entirely. This action would remove the vulnerable components and eliminate the potential for exploitation, providing the most comprehensive security solution.
Broader Implications and the Future of Abandoned Software
The Time4Popcorn incident serves as a stark reminder of the persistent dangers lurking within abandoned or poorly maintained software. As the digital landscape evolves at an unprecedented pace, applications that were once popular can become significant security liabilities if they are not regularly updated and patched. The ease with which the popcorntimeupd.xyz domain could be hijacked underscores the critical importance of domain registration and security for any service that relies on external updates.
This event also highlights the growing role of independent cybersecurity researchers and organizations like Eye Security and The Shadowserver Foundation in proactively identifying and mitigating large-scale threats. Their ability to identify, register, and then responsibly remediate vulnerabilities in abandoned software is a critical component of the modern cybersecurity ecosystem. The "sinkholing" of malicious domains and the delivery of remediation code, when executed ethically and legally, can prevent the creation of massive botnets and protect millions of unsuspecting users.
The incident also raises questions about the responsibility of developers, even those who abandon projects. While legal pressures can force the discontinuation of certain applications, the long-term security implications for users are often overlooked. A more robust framework for responsible software decommissioning, perhaps involving mandatory security audits or the transfer of ownership to dedicated security entities, could be a valuable consideration for the future.
Ultimately, the Time4Popcorn vulnerability and its successful remediation by Eye Security offer a valuable lesson: vigilance is paramount. Users must be aware of the software they install, understand the risks associated with outdated or unsupported applications, and prioritize the removal of potentially compromised programs from their devices. The digital world is dynamic, and while convenient tools can enhance our lives, they can also become vectors for attack if not managed with security in mind. The proactive stance taken by Eye Security, while commendable, should serve as a catalyst for increased user awareness and a renewed focus on the ongoing security of all digital assets.