Clarissa Hana
In a dramatic escalation of cyber warfare between prominent ransomware and extortion groups, the notorious ShinyHunters collective has successfully breached the data leak site of the Clop (also known as Cl0p) ransomware operation. The attack, which began on Friday night, resulted in the defacement of Clop’s Tor-based site and, according to ShinyHunters’ claims, the exfiltration of sensitive server data, including the private keys for Clop’s onion service. This incident marks a significant development, potentially shifting the power dynamics within the cybercrime ecosystem and raising serious questions about the security of even well-established ransomware operations.
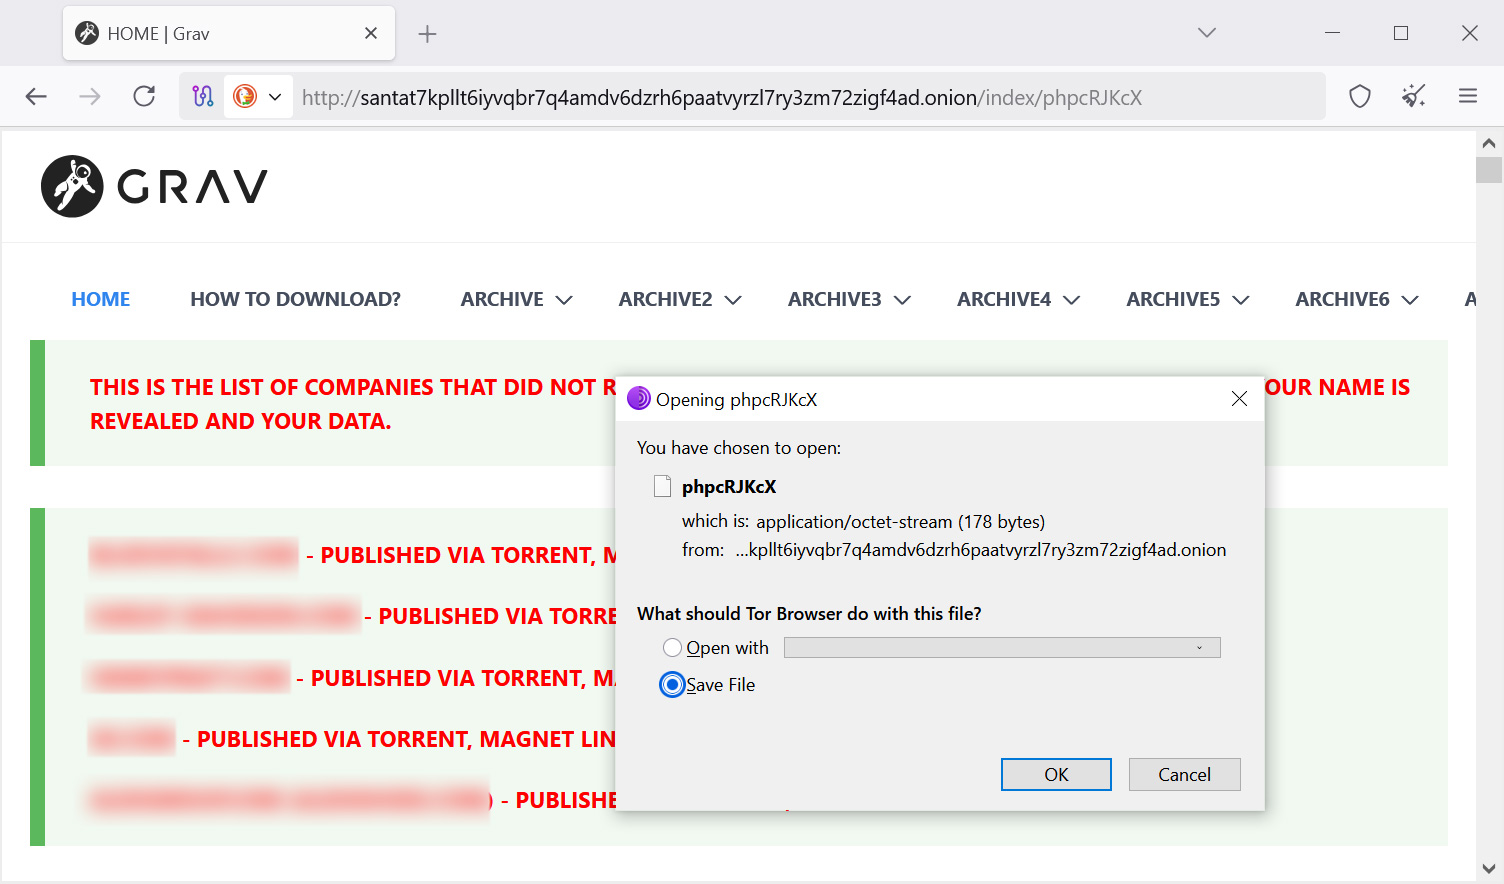
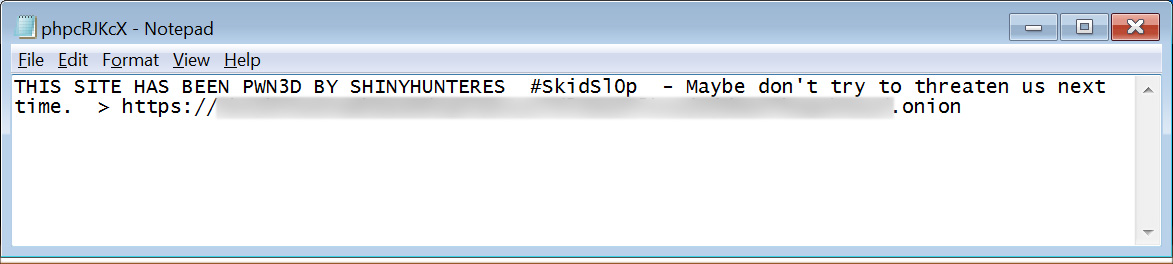
The breach reportedly commenced when ShinyHunters exploited what they described as an "unauthenticated file upload vulnerability" within the Grav Content Management System (CMS), the platform powering Clop’s data leak site. This vulnerability allowed ShinyHunters to upload a small text file to Clop’s servers, a move that served as an initial warning and a prelude to the more comprehensive defacement that followed. The initial file contained a defiant message directed at the Clop ransomware gang, explicitly stating, "THIS SITE HAS BEEN PWN3D BY SHINYHUNTERES #Skids10p – Maybe don’t try to threaten us next time." Accompanying this taunt was a direct link to ShinyHunters’ own data leak site, signaling a clear intent to retaliate and assert dominance.
BleepingComputer, a cybersecurity news outlet, independently confirmed the presence of this uploaded file on Clop’s server, verifying that it was accessible for download directly from the ransomware gang’s Tor site. This initial confirmation indicated a significant security lapse on Clop’s part, allowing an unauthorized entity to insert content into their infrastructure.
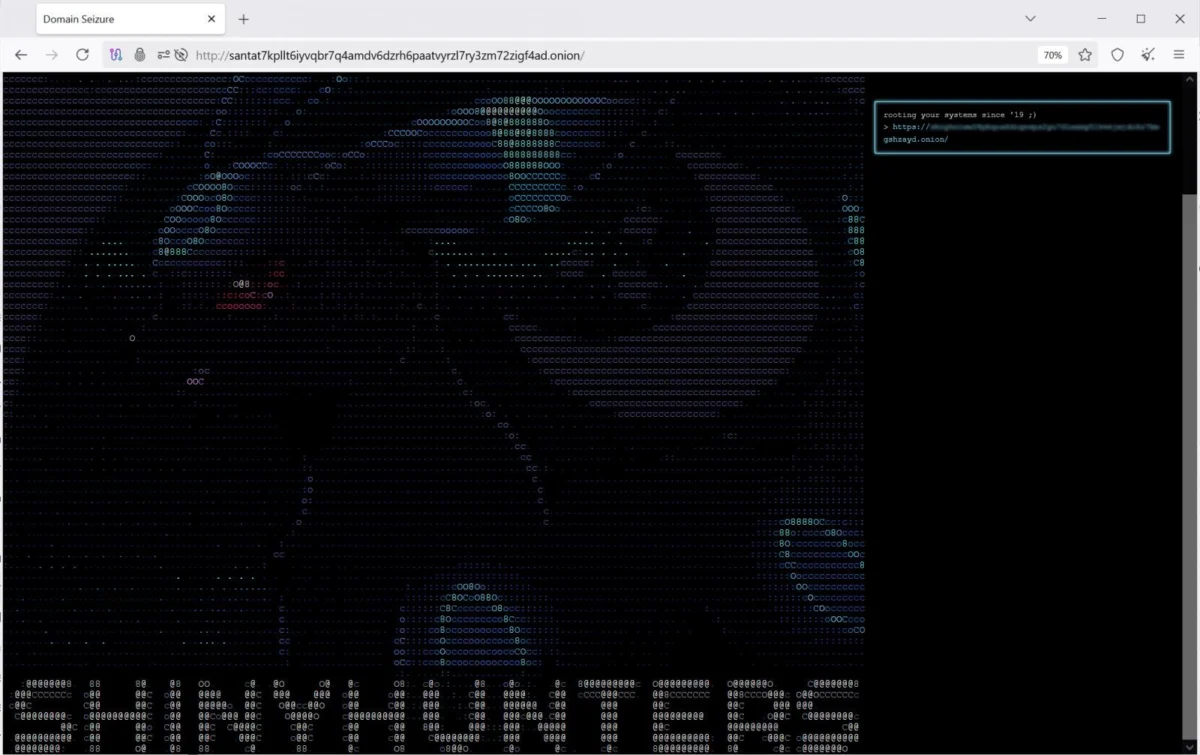
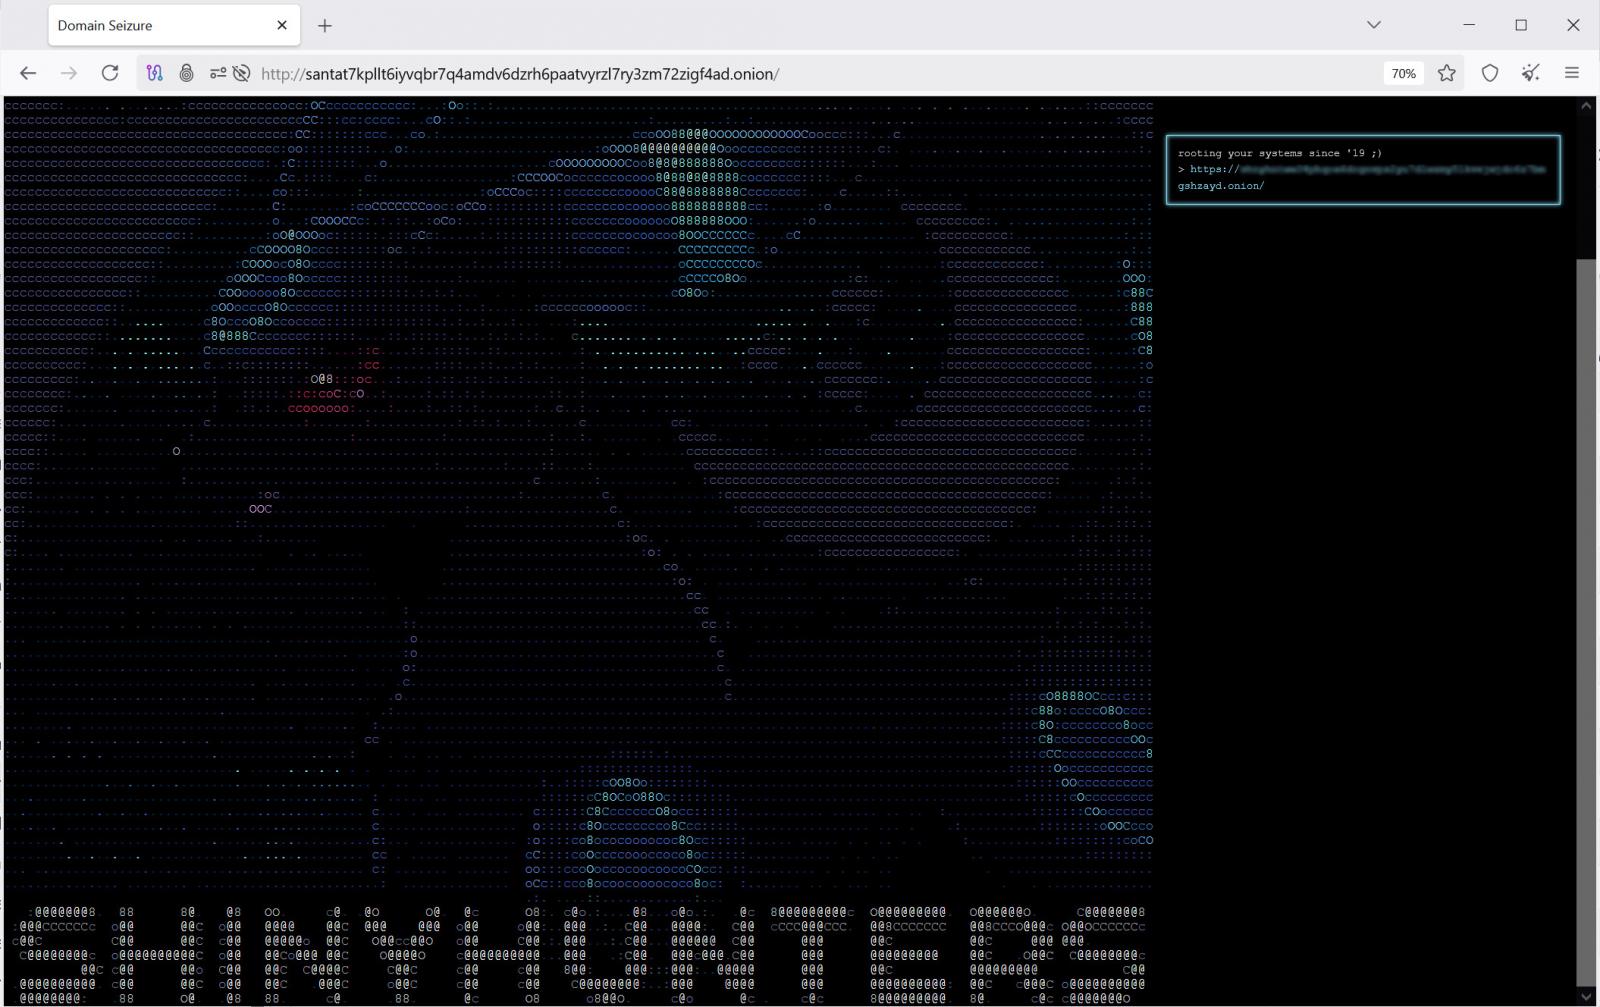
Several hours after this initial intrusion, ShinyHunters escalated their operation, announcing that they had "completely defaced" the Clop site. Upon visiting the site, it was evident that the original content had been replaced with a custom defacement page. This new page prominently featured ASCII art of Umbreon, a Pokémon character that serves as ShinyHunters’ distinctive logo. The defaced page also included a link back to the ShinyHunters Tor site and a taunting message: "rooting your systems since ’19 ;)". At the time of reporting, this defaced page remained active on Clop’s infrastructure, underscoring the success of ShinyHunters’ offensive.

Claims of Extensive Data Exfiltration
Beyond the defacement, ShinyHunters has made even more alarming claims regarding the extent of their access and the data they allegedly stole. The group informed BleepingComputer that they had gained "full access" to Clop’s server, leading to the exfiltration of a substantial amount of sensitive information. This reportedly includes source code, plugins for the Grav CMS, system logs, and other proprietary data.
"The data we stole includes source codes, gravCMS plugins, and other things. We are still downloading and reviewing them," ShinyHunters stated. The threat actors also asserted that they had secured all files located within the /var/log directory. This directory typically contains critical system activity logs, authentication records, and potentially the IP addresses of individuals who have accessed the server, offering a detailed glimpse into Clop’s operational infrastructure and user interactions.
Perhaps the most significant claim made by ShinyHunters is the alleged theft of the private keys for Clop’s Tor onion service. "We have their onion keys. So if they kick us out it wouldn’t matter at all because we control the private keys to host the same exact onion URL," a ShinyHunters representative boasted. If validated, this capability would grant ShinyHunters the power to operate a Tor site using Clop’s existing, established onion address on servers they control, effectively allowing them to impersonate or disrupt Clop’s primary communication channel. This would represent a severe blow to Clop’s operational security and their ability to maintain a secure presence on the dark web.
While BleepingComputer independently verified the defacement and the initial file upload, they have not yet independently corroborated ShinyHunters’ claims regarding the theft of server logs, source code, or the crucial private keys for Clop’s onion service. The group stated they are currently in the process of reviewing the exfiltrated data.
A New Extortion Play: Targeting a Fellow Criminal Enterprise
When questioned about their intentions for the stolen data, ShinyHunters explicitly stated their plan: "Going to extort them." This indicates a new dimension to the conflict, moving beyond simple retaliation to a direct financial motive. The group announced plans to publish a message on their own leak site, demanding that Clop contact them within 72 hours to negotiate. This move signifies a bold attempt to extort a ransomware operation that itself is known for its extortion tactics.
The defacement artwork, an Umbreon image, has historical significance within the cybercrime community. Cybersecurity researcher VXDB pointed out to BleepingComputer that this specific artwork was previously used in an August 2020 defacement of the HackForums website, an incident that ShinyHunters also claimed responsibility for at the time. This reuse of a signature element suggests a deliberate effort to reinforce their brand and past exploits.
The Genesis of the Feud: Retaliation and Allegations
ShinyHunters claims that this aggressive action is a direct act of retaliation for alleged threats made by a Clop representative. The current cyber conflict is reportedly an outgrowth of an ongoing feud between the two cybercrime entities. According to ShinyHunters’ narrative, a representative from Clop threatened to expose the identities of ShinyHunters’ members and made violent threats. These alleged threats were purportedly issued after ShinyHunters interfered with a Clop data theft campaign.
The roots of this escalating animosity appear to trace back to Clop’s 2025 data theft campaign targeting Oracle E-Business Suite (EBS) environments. In October 2025, Clop exploited multiple vulnerabilities in Oracle EBS servers, including a zero-day flaw tracked as CVE-2025-61882, to exfiltrate data from numerous organizations and initiate extortion schemes.
Coinciding with Clop’s exploitation, a group of threat actors operating under the moniker "Scattered Lapsus$ Hunters," which included ShinyHunters, released a proof-of-concept exploit. Oracle later confirmed that this exploit matched the one being used in the Clop attacks. At that time, ShinyHunters informed BleepingComputer that the exploit had originally belonged to them and that Clop had obtained it without authorization.
ShinyHunters alleges that tensions significantly heightened following the Oracle campaign. They claim that a Clop representative directly contacted them with menacing messages. "During the Oracle EBS campaign they ran and stole from me last year, someone from cl0p personally messaged me and said, and I quote (translated from Russian): I have more money than you and all of your people combined, I’ll kill you soon," ShinyHunters recounted.
BleepingComputer has not independently verified these specific allegations of personal threats. Efforts were made to contact Clop for comment regarding the breach and ShinyHunters’ accusations. As of the publication of this article, no response had been received from the Clop ransomware operation.
Broader Implications for the Cybercrime Landscape
The breach of Clop’s data leak site by ShinyHunters carries significant implications for the broader cybercrime landscape. It demonstrates that even established ransomware operations, which have historically relied on their own sophisticated infrastructure for data exfiltration and extortion, are vulnerable to attacks from other criminal actors. This incident could foster an environment of increased paranoia and infighting within the cybercriminal underworld, as groups may become more concerned about internal security and potential betrayals from rivals.
The claim of stealing private keys for an onion service is particularly noteworthy. If confirmed, it highlights a sophisticated level of attack that goes beyond simple website defacement. The ability to potentially hijack a dark web domain represents a potent tool for disruption and misinformation. It also suggests that the lines between different types of cybercrime, such as ransomware operations and data extortion gangs, are becoming increasingly blurred, with groups engaging in multi-faceted attacks against each other.
The alleged motivation for the attack – retaliation for threats – also underscores the complex and often personal dynamics that can drive actions within cybercriminal communities. While often perceived as purely transactional, these groups can also be driven by ego, perceived slights, and a desire for revenge.
The potential for ShinyHunters to extort Clop introduces a new dynamic. It normalizes the idea of cybercriminal groups targeting each other for financial gain, moving beyond ideological or retaliatory motives. This could lead to a cycle of attacks and counter-attacks, with groups seeking to profit from the vulnerabilities of their peers.
The security industry will be closely watching for any further developments, particularly any independent verification of ShinyHunters’ claims regarding the stolen data and private keys. The outcome of this internal conflict within the cybercrime world could have unforeseen consequences for the broader cybersecurity landscape, potentially influencing attack methodologies and the stability of various criminal enterprises. The fact that a group known for data theft has successfully infiltrated and potentially compromised the operational infrastructure of a major ransomware player signals a maturing, albeit more dangerous, phase of cyber warfare.