Clarissa Hana
The development marks a significant stride in the ongoing global crackdown on ShinyHunters, a group that has consistently posed a substantial threat to organizations worldwide through extensive data theft and subsequent extortion campaigns. Khader’s alleged cooperation is considered "critical" by law enforcement officials, offering a potential pathway to identifying and apprehending other high-ranking members of the cybercriminal enterprise.
Timeline of Events and Key Developments
The reported detention of Khader, also known as "Rey," occurred this week, with specific accounts pointing to his apprehension on Tuesday. This arrest follows a series of high-profile cyber incidents and a dedicated investigative push by the FBI against the ShinyHunters group.
-
September 2023: ShinyHunters claims responsibility for a significant cyberattack against the FBI itself. The group alleges they exploited a zero-day vulnerability in Oracle’s PeopleSoft system to gain initial access, subsequently moving laterally into FBI-managed AWS GovCloud environments. The threat actors claimed to have exfiltrated between 2 to 3 terabytes of sensitive data, purportedly including information on current and former FBI employees, job applicants, and internal medical and psychiatric records. While the FBI acknowledged investigating unauthorized activity, they did not confirm the extent of the data breach.
-
September 15, 2023: In the wake of the alleged FBI breach, Dutch police arrested a 24-year-old man in Amsterdam. This individual, identified by security researchers as Pepijn van der Stap, formerly known online as "Umbreon," was taken into custody as part of an investigation into ShinyHunters.
-
Following Van der Stap’s Arrest: The FBI issued a public warning to other ShinyHunters members, urging them to surrender to authorities. Assistant Director of the FBI Cyber Division, Brett Leatherman, emphasized the increasing certainty of apprehension, stating, "Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left." He added, "The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out first while the choice is still yours."
-
Early October 2023 (around the time of Khader’s reported detention): Signs of significant disruption within ShinyHunters’ operational infrastructure began to emerge. An individual identified as a ShinyHunters affiliate, who had previously communicated with media outlets regarding the FBI attack and a data breach involving the Clop ransomware gang, abruptly deactivated their online messaging accounts. Subsequently, the ShinyHunters data leak site went offline, and the group’s primary representative ceased responding to media inquiries, including those from Reuters and BleepingComputer.
-
October 2023 (Days following Khader’s reported detention): A new ShinyHunters data leak site surfaced, indicating that other members of the group may be continuing the extortion operation.
The Identity and Role of "Rey"
The threat actor known online as "Rey" has been a recurring and significant presence in the cybercrime landscape over the past two years. His alleged involvement in numerous high-profile data theft and extortion attacks has made him a person of interest for law enforcement agencies globally.
-
January 2025 (Reported): Rey, along with three other threat actors, claimed responsibility for breaching the internal Jira ticketing system of Telefónica. Approximately 2.3GB of documents, tickets, and other data were reportedly stolen. At the time, Rey was identified as a member of the nascent HellCat ransomware operation, which also targeted Jira servers at various organizations worldwide.
-
February 2025 (Reported): Orange confirmed a cyberattack on its Romanian operations, with Rey leaking around 6.5GB of stolen data. Rey stated to BleepingComputer that he was a member of HellCat but had conducted the Orange breach independently.
-
Later Association with ShinyHunters: Rey was subsequently linked to the ShinyHunters extortion group. He was observed to have administrative privileges within Telegram channels managed by "Scattered Lapsus$ Hunters," a group that emerged in 2025 and claimed to comprise former members of prominent cybercrime syndicates like Lapsus$, Scattered Spider, and ShinyHunters.
-
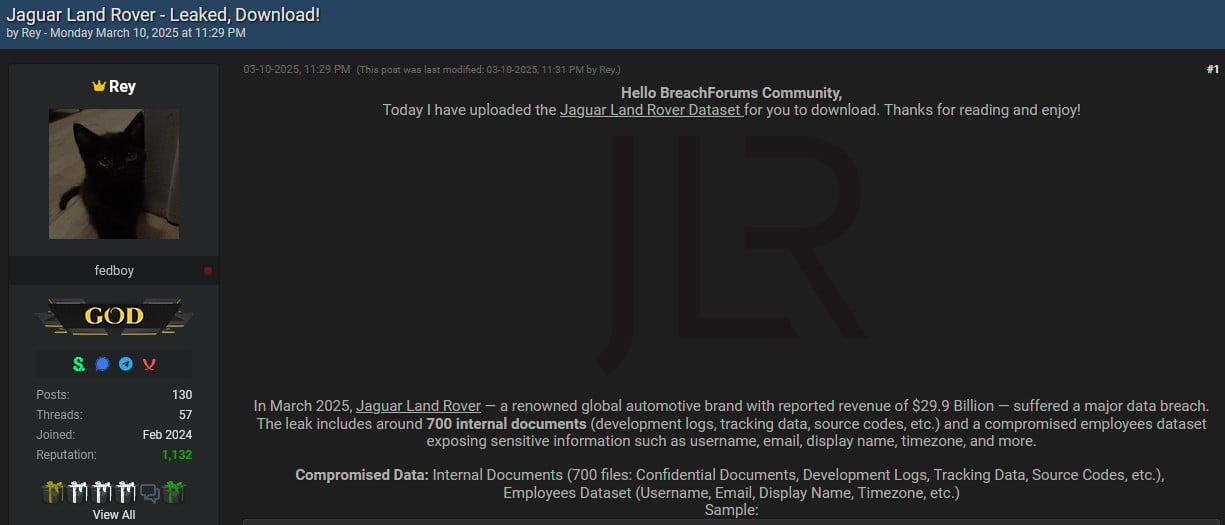
Scattered Lapsus$ Hunters and Jaguar Land Rover: This collective claimed responsibility for the September 2025 cyberattack on Jaguar Land Rover, an incident that forced the automaker to halt production for weeks and resulted in an estimated financial loss exceeding $220 million. Rey was also implicated in an earlier March 2025 breach of Jaguar Land Rover, where he allegedly leaked gigabytes of sensitive data, including Jira issues, source code, employee information, and development logs.
-
November 2025 and Cooperation with Law Enforcement: Security journalist Brian Krebs reported in November 2025 that "Rey" was indeed Saif Al-Din Khader. Krebs’s investigation, which involved analyzing information from infostealer logs and direct communication with Khader via Signal, revealed that Khader had been attempting to distance himself from Scattered Lapsus$ Hunters and claimed to have been cooperating with law enforcement since at least June of that year. Khader reportedly stated to Krebs, "I’m already cooperating with law enforcement. In fact, I have been talking to them since at least June. I have told them nearly everything. I haven’t really done anything like breaching into a corp or extortion related since September." Krebs noted that these claims could not be independently verified at the time.
The Significance of Khader’s Cooperation
The cooperation of an individual like Khader, who allegedly possesses intimate knowledge of ShinyHunters’ operations, digital infrastructure, and member identities, could prove invaluable to law enforcement. By analyzing his electronic devices and digital communications, investigators aim to piece together a comprehensive picture of the group’s hierarchy, operational methods, and financial dealings.
"His cooperation is critical to ongoing efforts to arrest these hackers," a source familiar with the investigation told Reuters. The ability to trace digital footprints, understand communication channels, and identify co-conspirators is paramount in disrupting sophisticated cybercriminal organizations.
ShinyHunters’ Modus Operandi and Historical Operations
The ShinyHunters gang has established a notorious reputation for its aggressive and far-reaching cyberattacks. Their primary tactic involves breaching third-party integration companies, often leveraging stolen authentication tokens to gain unauthorized access to connected Software-as-a-Service (SaaS) environments. This method has enabled them to conduct massive data theft operations against a wide array of organizations.
Their targets have spanned various sectors, with a notable focus in recent years on Salesforce and other cloud-based SaaS platforms. Significant breaches attributed to ShinyHunters include:
-
Salesforce and Associated Breaches: Attacks linked to Salesforce environments have impacted major entities such as Google, Cisco, and PornHub. In these instances, the group often breaches an intermediary service provider to gain access to sensitive customer data stored within these cloud platforms.
-
Instructure Canvas Attack: In May 2023, ShinyHunters executed a large-scale data theft attack against Instructure Canvas, a learning management system used by thousands of educational institutions. This incident led to significant platform disruptions, and Instructure eventually reached an "agreement" with the threat actors to prevent the leaked data from being published.
-
Snowflake Data-Theft Attacks: The group has also been linked to data theft incidents affecting Snowflake customers, with investigations and indictments in the U.S. pointing to their involvement in extorting millions of dollars from victims.
-
PowerSchool Breaches: ShinyHunters has also been implicated in breaches at PowerSchool, a widely used student information system, contributing to the ongoing threat to educational data.
-
Breached v2 Hacking Forum: The group’s activities have also extended to the operation of hacking forums, with arrests linked to the administration of the Breached v2 forum.
The detention of Saif al-Din Khader, coupled with the previous arrest in the Netherlands and the FBI’s intensified efforts, signals a significant shift in the landscape for the ShinyHunters organization. While the emergence of a new leak site suggests resilience from some elements of the group, the pressure from law enforcement and the potential for further internal cooperation pose an escalating risk to those who remain involved. The coming weeks and months will likely reveal the full impact of Khader’s cooperation on the future of ShinyHunters and its ability to continue its global campaign of cyber extortion.