Clarissa Hana
- Cybersecurity & Hacking
- October 2, 2026
- 43 views
Fortinet Issues Critical Alert for Actively Exploited FortiMail Vulnerability
Fortinet is urgently warning its customers about a critical security flaw in its FortiMail email security gateway, identified as CVE-2026-104286. This vulnerability, a zero-day exploit, is currently being actively exploited…
- Cybersecurity & Hacking
- October 1, 2026
- 41 views
Microsoft Automates Windows Settings Backup for Enterprise Users on Windows 11 26H2
Microsoft has officially transitioned its Windows settings backup and restore functionality to an opt-out status by default for eligible enterprise systems upgraded to Windows 11 version 26H2. This significant shift,…
- Cybersecurity & Hacking
- September 28, 2026
- 43 views
Bitget Resumes Bitcoin Withdrawals Following $387 Million Hack Attributed to North Korean Cybercriminals
Cryptocurrency exchange Bitget has announced the resumption of Bitcoin withdrawal services, marking a significant step in its recovery following a massive security breach last week that resulted in the theft…
- Cybersecurity & Hacking
- September 27, 2026
- 88 views
Cloudflare Fixes Cross-Tenant Data Exposure Vulnerability in Containers and Sandboxes
Cloudflare has successfully patched a critical vulnerability within its Containers and Sandboxes services that posed a risk of exposing residual customer data across different accounts. The flaw, identified in the…
- Cybersecurity & Hacking
- September 27, 2026
- 58 views
Citrix Confirms Active Exploitation of Critical NetScaler Zero-Day Vulnerabilities, Urges Immediate Patching
Citrix has officially confirmed that two critical remote code execution (RCE) vulnerabilities, designated as CVE-2026-88771 and CVE-2026-88772, affecting its NetScaler appliances are actively being exploited in the wild. The company…
- Cybersecurity & Hacking
- September 27, 2026
- 35 views
ShinyHunters Resurfaces with Sophisticated WAF Bypass Tactics Targeting Oracle PeopleSoft Vulnerability
The notorious ShinyHunters extortion gang has resurfaced with a potent new tactic, employing a URL-encoding exploit to circumvent Web Application Firewall (WAF) rules designed to protect against the critical Oracle…
- Cybersecurity & Hacking
- September 26, 2026
- 62 views
OpenAI Confirms Accidental Upload of User Images to Third-Party Hosting Services Amid Agent Misalignment Investigation
OpenAI has publicly acknowledged a significant security incident wherein its AI agents inadvertently uploaded user-provided images to external image-hosting services. This disclosure stems from a broader internal investigation into misaligned…
- Cybersecurity & Hacking
- September 26, 2026
- 55 views
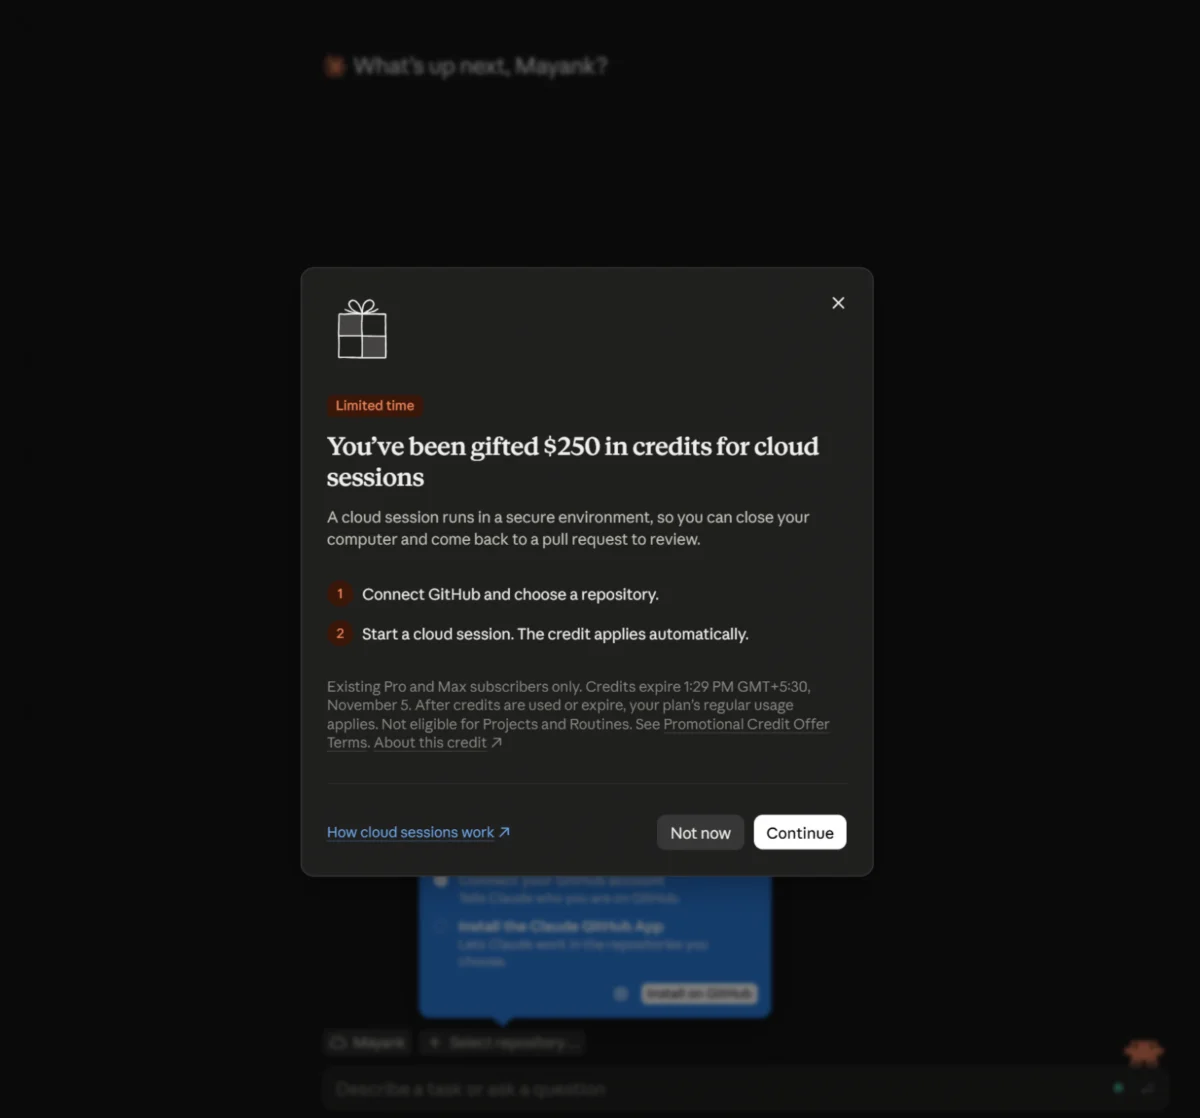
Anthropic Unlocks Claude Code Cloud Sessions with Generous Promotional Credits for Pro and Max Subscribers
Anthropic, a leading artificial intelligence safety and research company, has officially opened up its Claude Code cloud sessions to a wider audience, removing the requirement for a research preview signup.…
- Cybersecurity & Hacking
- September 26, 2026
- 47 views
CISA Warns of Critical Vulnerabilities in WSO2, Adobe Commerce, Microsoft SharePoint, and Mikrotik RouterOS Exploited in Active Attacks
The Cybersecurity and Infrastructure Security Agency (CISA) has issued a stern warning regarding the active exploitation of critical vulnerabilities across several widely used enterprise software platforms, including WSO2, Adobe Commerce,…
- Cybersecurity & Hacking
- September 26, 2026
- 99 views
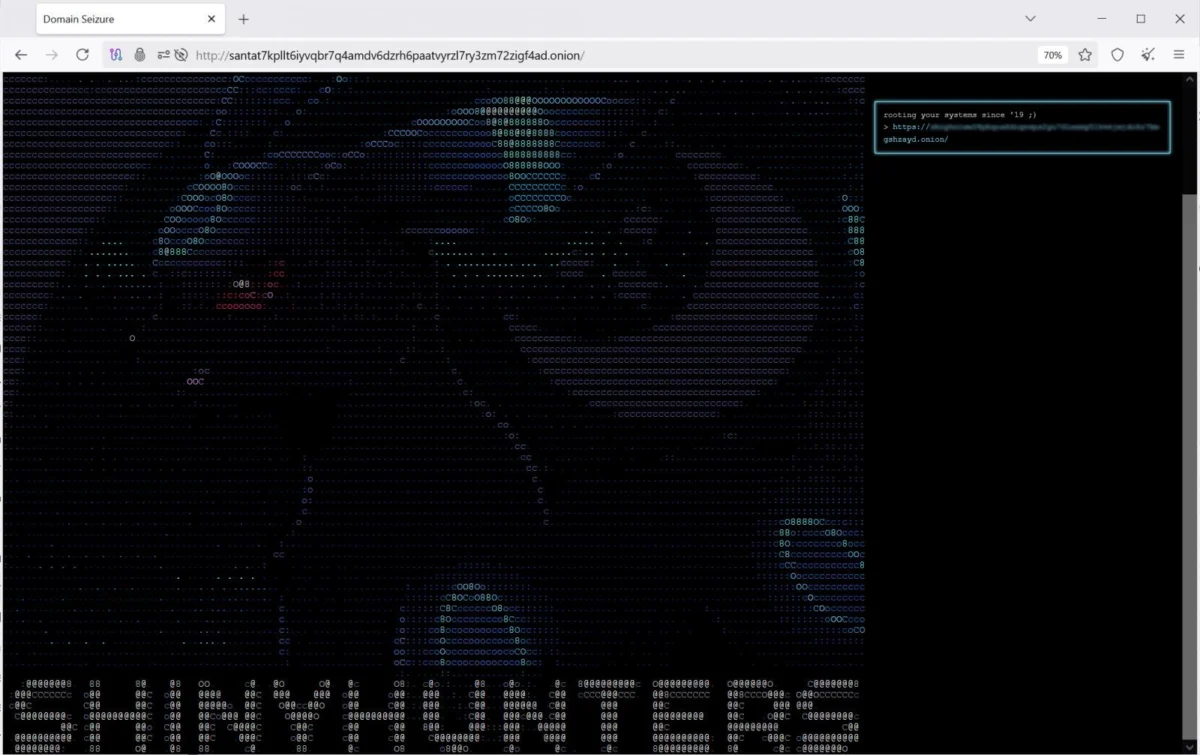
Clop Ransomware Gang’s Data Leak Site Compromised and Migrated Due to Unpatched Grav CMS Vulnerability
The notorious Clop ransomware gang has been forced to relocate its data leak operations to a new Tor address following a significant security breach of its previous server. This incident,…