Clarissa Hana
- Cybersecurity & Hacking
- September 23, 2026
- 98 views
Hackers Start Exploiting Critical WordPress Flaw for Code Execution
Threat actors have escalated their activities from merely probing WordPress websites vulnerable to CVE-2026-87902, a critical unauthenticated path traversal bug, to actively exploiting the flaw for remote code execution (RCE).…
- Cybersecurity & Hacking
- September 23, 2026
- 66 views
Arista Networks Addresses Actively Exploited Zero-Day Vulnerability in VeloCloud Orchestrator
Arista Networks has issued urgent security patches for a critical zero-day vulnerability that is currently being actively exploited in the wild, impacting on-premises deployments of its VeloCloud Orchestrator (VCO). This…
- Cybersecurity & Hacking
- September 23, 2026
- 99 views
Sweden Fines Miljodata $183,000 Over Data Breach Affecting 2.2 Million Individuals
Sweden’s data privacy authority, the Integrity Protection Authority (IMY), has levied a substantial fine of SEK 1.8 million, equivalent to approximately $183,000 USD, against IT systems provider Miljodata. This penalty…
- Cybersecurity & Hacking
- September 23, 2026
- 88 views
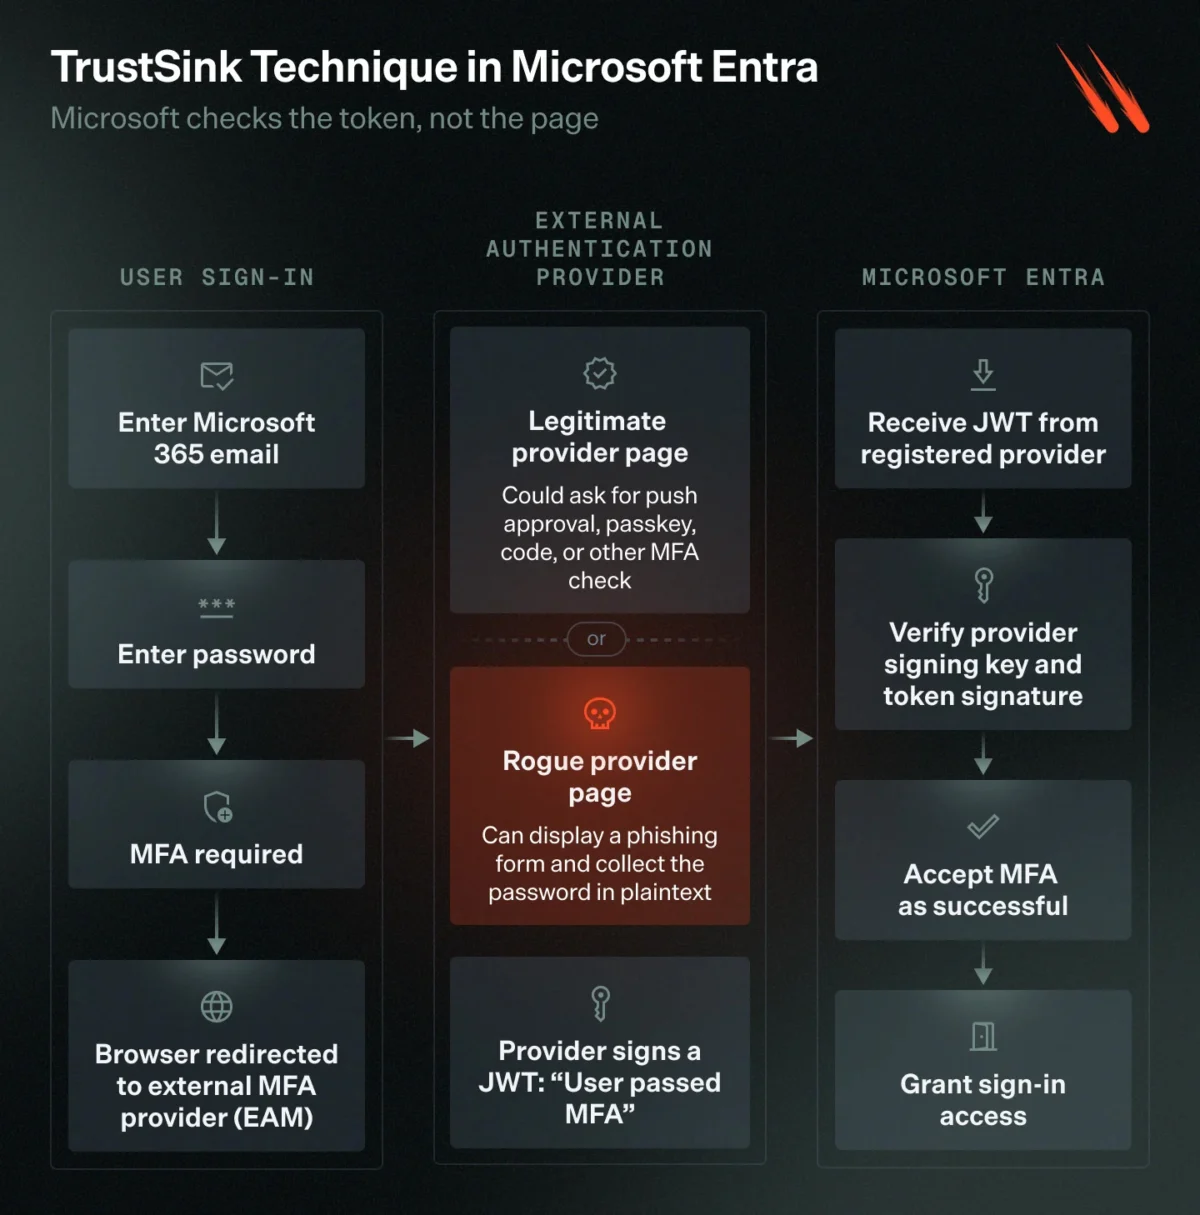
TrustSink Attack Leverages Compromised Privileged Accounts to Hijack Multifactor Authentication and Steal Passwords
Security researchers have unveiled a sophisticated attack dubbed "TrustSink" that exploits a critical vulnerability in how Microsoft Entra ID (formerly Azure Active Directory) integrates with external multifactor authentication (MFA) providers.…
- Cybersecurity & Hacking
- September 22, 2026
- 50 views
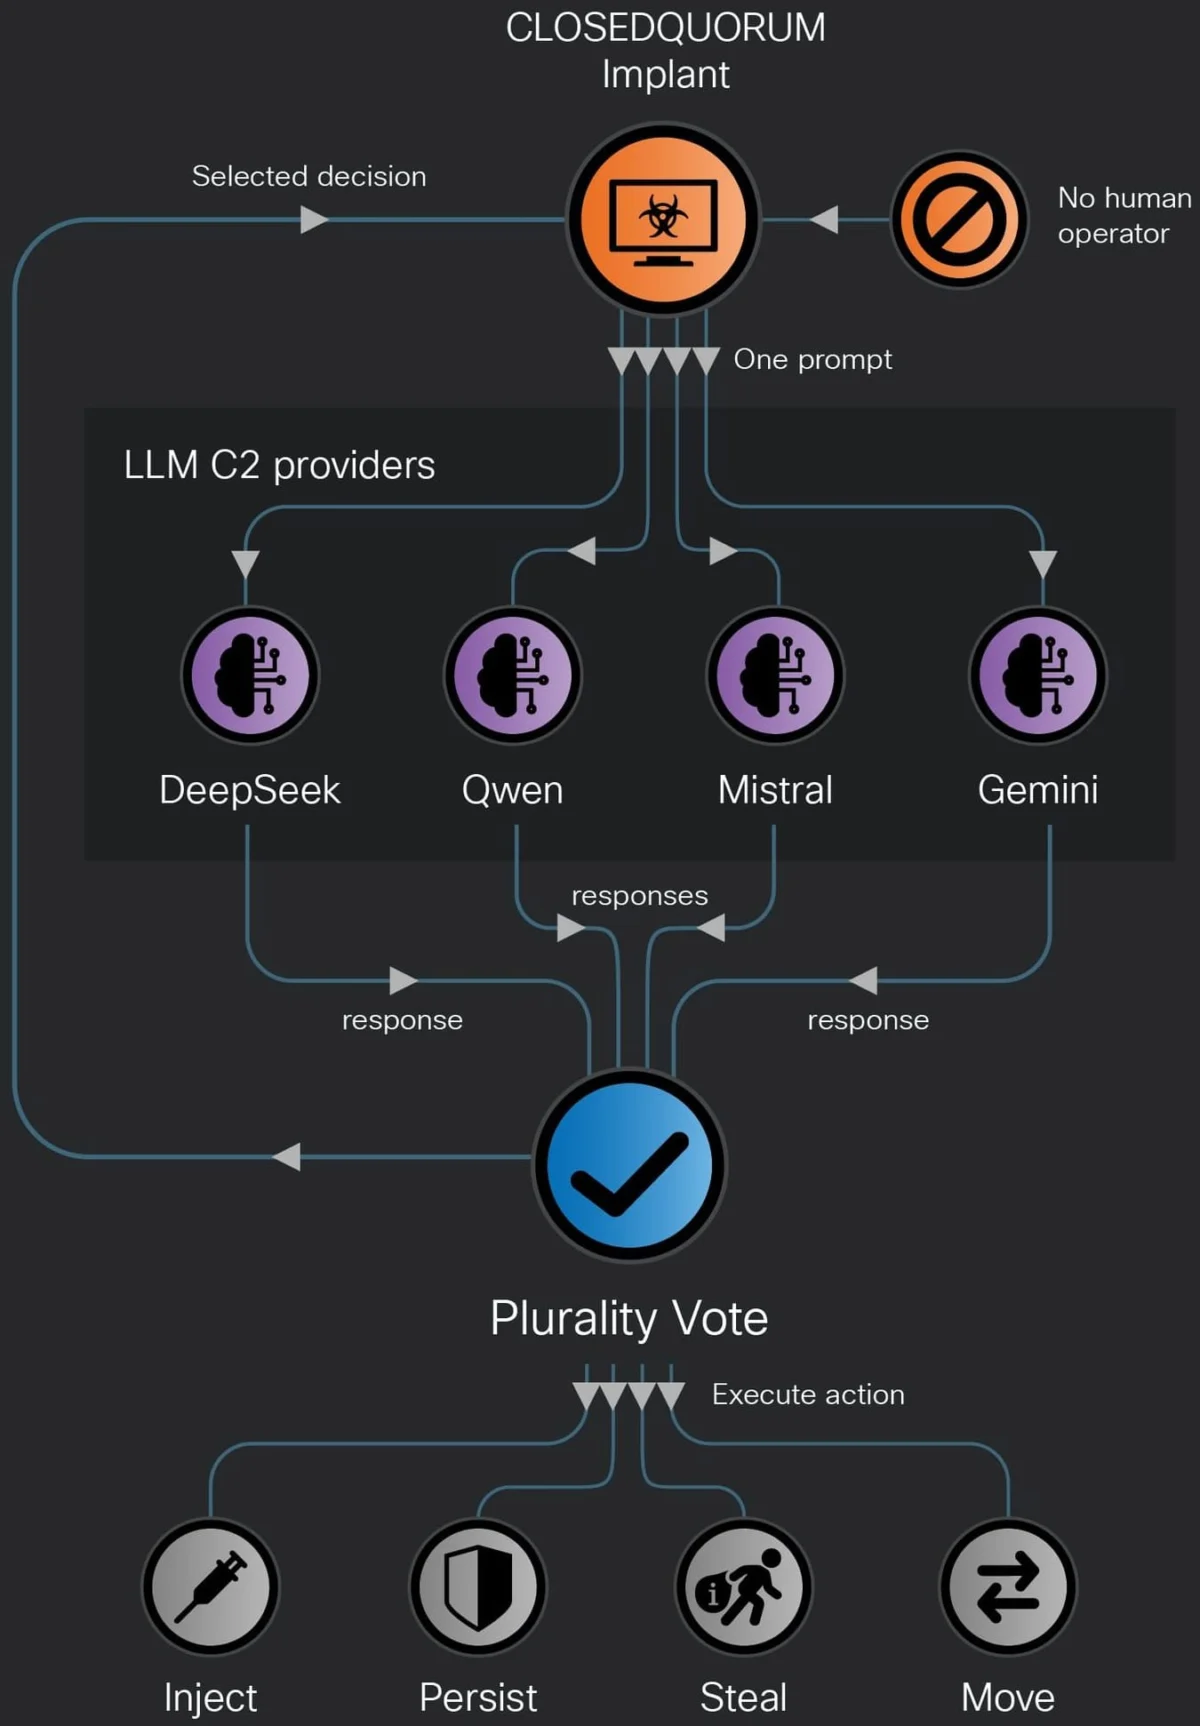
ClosedQuorum: The Dawn of Autonomous AI-Driven Malware in Windows Environments
A groundbreaking development in the cybersecurity landscape has emerged with the identification of a new Windows malware, codenamed ClosedQuorum, which leverages advanced artificial intelligence models to autonomously orchestrate post-compromise attack…
- Cybersecurity & Hacking
- September 22, 2026
- 48 views
Microsoft Defender Faces New Threat as Researcher Releases Exploit to Block Antivirus Updates
Over the weekend, security researcher Abdelhamid Naceri, widely known in cybersecurity circles as "Nightmare Eclipse," unveiled a new exploit targeting Microsoft Defender, the built-in antivirus solution for Windows operating systems.…
- Cybersecurity & Hacking
- September 22, 2026
- 53 views
CISA Alerts of Active Exploitation of Three Linux Kernel Flaws, Including a Critical Vulnerability
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a stark warning to federal agencies, revealing that three critical vulnerabilities within the Linux kernel are currently being actively exploited…
- Cybersecurity & Hacking
- September 22, 2026
- 66 views
BigCommerce Merchants Alerted to Data Breach Linked to Compromised Ribon App Credentials
An extensive data breach has impacted numerous merchants operating on the BigCommerce e-commerce platform, following the compromise of credentials for third-party applications developed by Ribon. Attackers exploited these compromised credentials…
- Cybersecurity & Hacking
- September 21, 2026
- 46 views
Microsoft’s September 2026 Security Updates Cause Widespread File History Backup Failures Across Windows Versions
Microsoft has issued a critical alert to users of its Windows operating system, warning that the built-in File History backup feature may cease to function correctly on a significant number…
- Cybersecurity & Hacking
- September 21, 2026
- 47 views
Microsoft Teams Enhances Security with Customizable Malware File Blocking and Expanded Administrator Controls
Microsoft Teams is set to significantly bolster its security posture with an upcoming update that will empower administrators to customize the list of file extensions recognized as potential malware and…