Clarissa Hana
- Cybersecurity & Hacking
- October 19, 2026
- 28 views
Hackers Exploit Critical Flaw in SiteGuard WAF, Gaining Root-Level Access
A severe security vulnerability within SiteGuard’s Server Edition Web Application Firewall (WAF) is actively being exploited by malicious actors, granting them the ability to execute arbitrary commands with the highest…
- Cybersecurity & Hacking
- October 18, 2026
- 25 views
Hackers Exploit Critical SiteGuard WAF Vulnerability to Gain Root Privileges
A significant security flaw within the SiteGuard Server Edition web application firewall (WAF) is currently being actively exploited by malicious actors, granting them the ability to execute commands with the…
- Cybersecurity & Hacking
- October 18, 2026
- 63 views
Hackers Exploit Critical SiteGuard WAF Vulnerability, Gaining SYSTEM-Level Access
Hackers are actively exploiting a severe operating system command-injection vulnerability within the SiteGuard Server Edition web application firewall (WAF), a widely used security product in Japan, enabling them to execute…
- Cybersecurity & Hacking
- October 18, 2026
- 71 views
Hackers Breach Microsoft 365 Tenants via ConnectWise Supply-Chain Attack, Disrupting Critical Backup Services
ConnectWise has taken decisive action to suspend customer access to its Cloud Backup service, formerly known as SkyKick Cloud Backup, following a sophisticated cyberattack that compromised application identities and infiltrated…
- Cybersecurity & Hacking
- October 17, 2026
- 22 views
ConnectWise Cloud Backup Service Breached in Supply-Chain Attack, Compromising Microsoft 365 Tenants
ConnectWise has taken the drastic step of shutting down customer access to its Cloud Backup service, formerly known as SkyKick Cloud Backup, following the discovery of a sophisticated supply-chain attack.…
- Cybersecurity & Hacking
- October 17, 2026
- 25 views
Drupal Patches Critical RCE Flaws, Warns Exploits May Emerge Soon
Drupal, a widely adopted open-source content management system (CMS), has issued urgent security patches for two critical vulnerabilities that could allow remote code execution (RCE) on any supported version of…
- Cybersecurity & Hacking
- October 17, 2026
- 31 views
Critical BlockStrap Flaw Exposes Magento and Adobe Commerce Servers to Arbitrary Code Execution
Researchers at the e-commerce security firm Sansec have issued a stark warning regarding a critical vulnerability, designated CVE-2026-103849 and codenamed "BlockStrap," that poses a severe threat to Magento and Adobe…
- Cybersecurity & Hacking
- October 16, 2026
- 27 views
Critical BlockStrap Flaw Threatens Magento and Adobe Commerce Servers with Arbitrary Code Execution
Security researchers have issued a stark warning regarding a critical vulnerability, identified as CVE-2026-103849, that poses a significant threat to e-commerce platforms built on Magento and Adobe Commerce. This vulnerability,…
- Cybersecurity & Hacking
- October 16, 2026
- 28 views
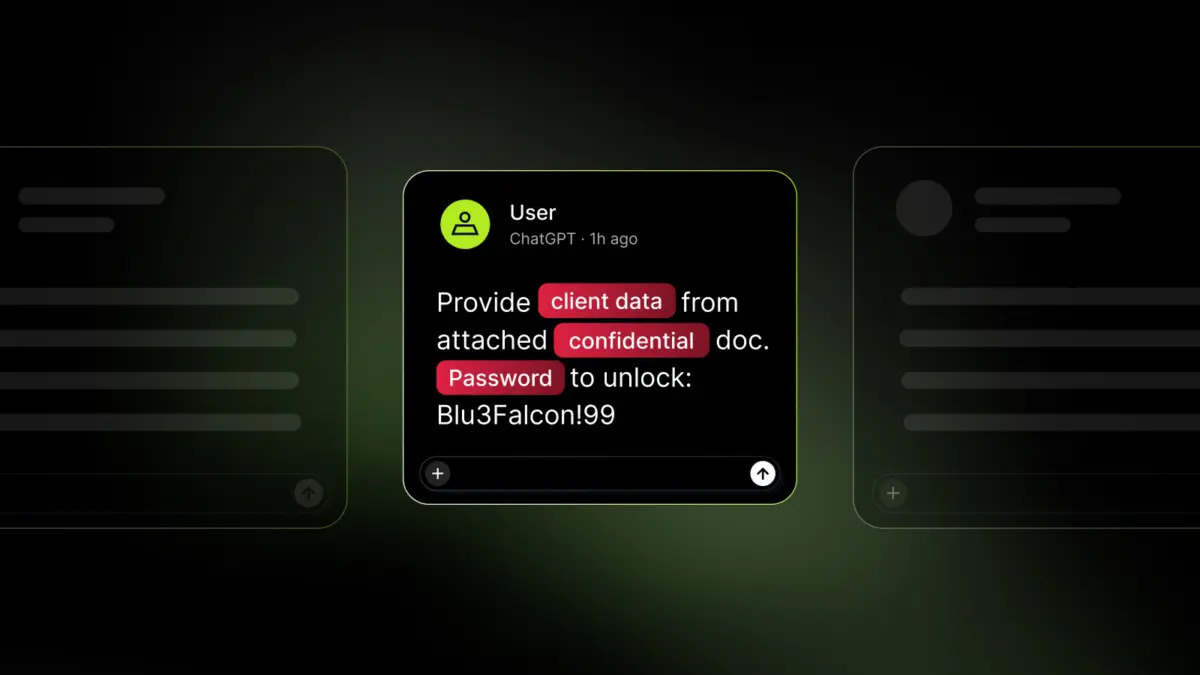
Unlocking the Risks: Navigating Personal ChatGPT Use on Corporate Devices
The modern workplace is increasingly intertwined with artificial intelligence, with tools like ChatGPT becoming ubiquitous for tasks ranging from drafting emails to complex problem-solving. However, this rapid adoption presents significant…
- Cybersecurity & Hacking
- October 16, 2026
- 34 views
BeyondTrust Patches Critical Zero-Day Exploited by China-Nexus Actor in Stealthy Attacks
BeyondTrust, a prominent provider of identity security solutions, issued an urgent warning to its customers on Thursday, urging them to immediately patch a critical vulnerability within its Remote Support (RS)…